
24/7 Managed Detection & Response
Detect, Investigate and Contain Under Your Response Plan
Monitoring, analyst investigation and preauthorized containment across your agreed endpoints, identities, Microsoft 365 and cloud sources, 24 hours a day. Your response plan defines the actions we can take, when we escalate and what your team owns.
Our analysts investigate suspicious activity from agreed sources, escalate validated findings and carry out containment actions authorized in your response plan. Broader forensics, eradication and recovery are scoped separately.


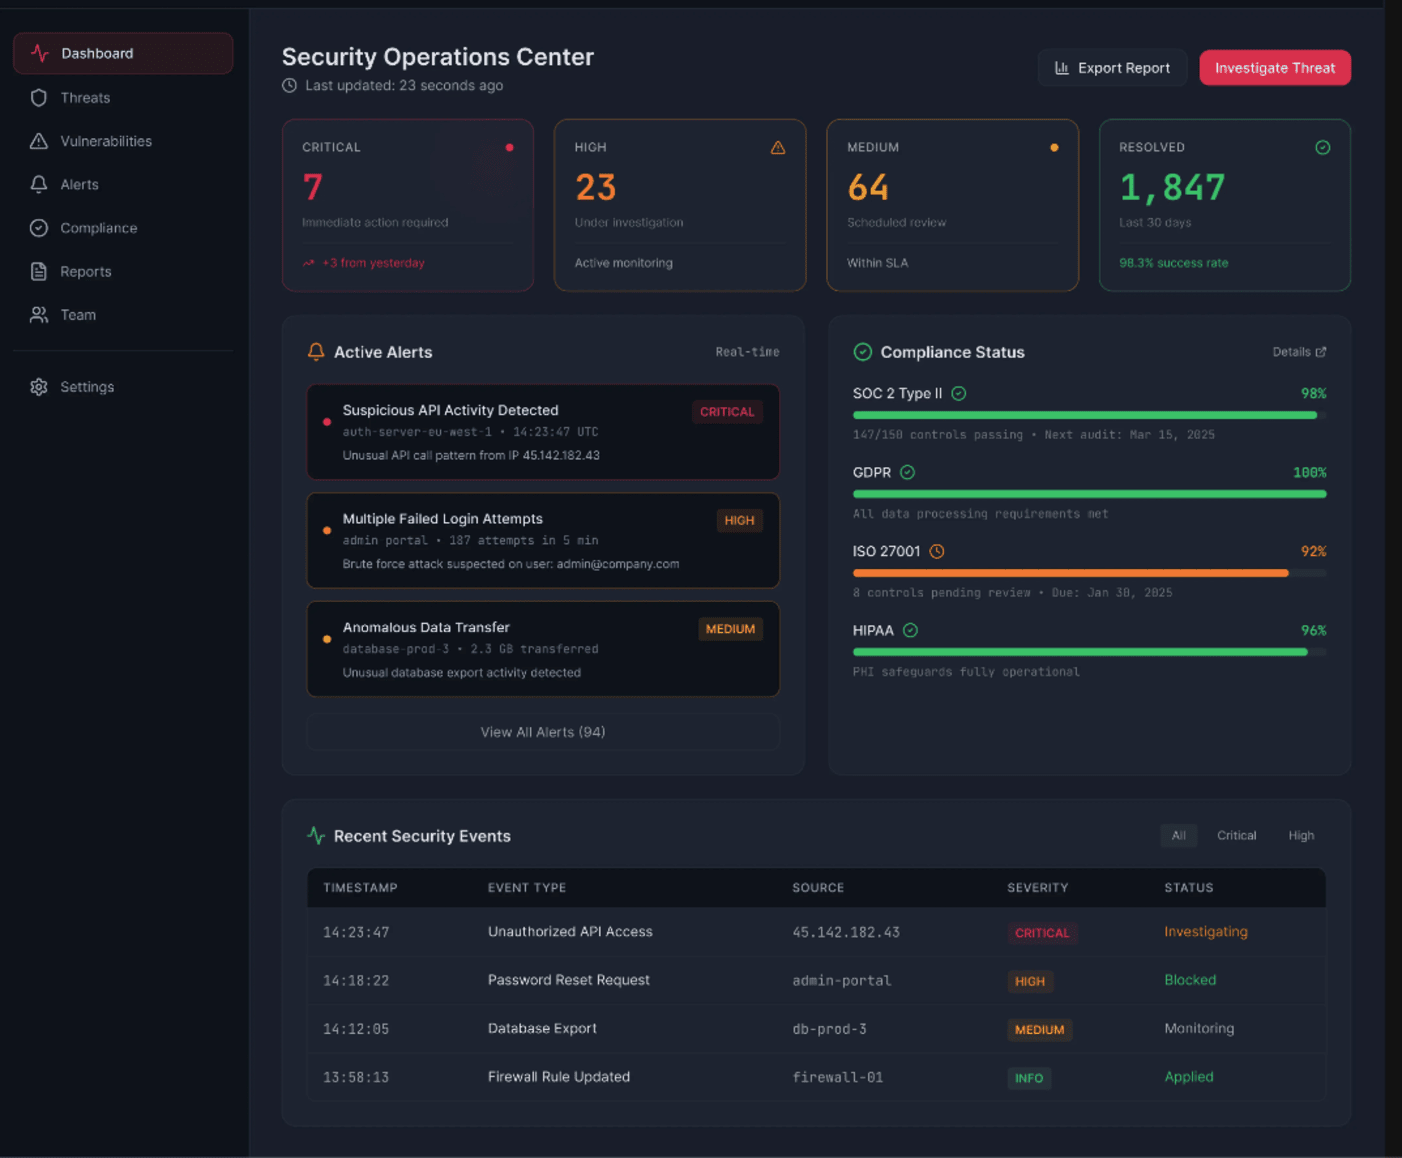
Ransomware hits you on Sunday at 2AM!
Who is protecting you?
Coverage summary
Managed detection and response at a glance
24/7 SOC monitoring, managed detection and response, and automated response playbooks across your agreed environment. Containment authority and escalation are defined in your response plan.
What we monitor
Endpoints, identities, Microsoft 365 and the cloud environments agreed at onboarding.
Hours
24/7, including nights, weekends and holidays.
Onboarding
We agree scope, connect data sources, tune detections and write the response plan with you before monitoring starts.
Reporting
Escalations in plain language, plus regular reporting your leadership and board can read.
Who does what
Why Traditional IT Security is Failing You
Buying more security tools won't save you if you lack the human intelligence to run them. Most organizations are drowning in alerts, exposed after hours, and lack the controls to actually contain an active threat.
Here is how Cloudskope closes the gap.

Drowning in Alerts. Starving for Action


We cut through the noise. Instead of burying your team in false positives, our analysts investigate anomalies and only escalate verified threats equipped with clear remediation steps.

The Attack Surface Has Evolved
We extend enterprise-grade visibility beyond laptops and servers, monitoring Microsoft 365, cloud infrastructure, and administrative behavior to catch adversaries wherever they hide.

Identity & Account Takeover
We lock down the front door. Cloudskope monitors for suspicious sign-ins, mailbox abuse, and rogue privilege escalations to prevent Business Email Compromise (BEC).

Visibility Without Containment is Flawed
We don't just tell you you're under attack; we act on it. We pair threat hunting with defined containment playbooks and SOAR automation to isolate compromised assets and block lateral movement.
The 2:00 AM Sunday Problem
A 9-to-5 IT team cannot watch a 24/7 adversary. Our SOC monitors the agreed sources 24/7/365, including nights, weekends and holidays, with analyst triage and preauthorized containment defined in your response plan.

Enterprise Security Without Building a SOC
Skip the payroll build-out and the hiring market. Our SOC analysts monitor your agreed environment around the clock and report to your leadership in plain terms.
Our MDR Arsenal:
Active Defense, Not Passive Alerts.
Most MDR providers are just alert factories. They watch your network and hand you a ticket when something breaks.
Cloudskope is different. We combine 24/7 threat hunting, analyst-led triage and containment authorized in your response plan to detect threats earlier and limit their spread.

24/7/365 Threat Hunting
Hackers don't sleep. Neither do we.
Experienced SOC analysts monitor your environment around the clock. We don't just wait for automated alarms; we actively hunt for hidden adversaries and anomalies across the sources agreed in your coverage.
Attackers deliberately schedule their most devastating ransomware deployments for 3:00 AM on Sundays and major holidays. If you aren't hunting around the clock, you are leaving your vault door wide open when it matters most.
Continuous Adversary Pursuit
Continuous Monitoring Of Agreed Sources
Analyst Triage Of Anomalies
Improvement Recommendations

Signal Over Noise: Human-Led Triage
Stop drowning in false positives.
We do not just forward raw alerts. Our analysts triage suspicious signals, correlate the evidence and filter out the noise. When we escalate a threat to your team, it has been validated and comes with recommended remediation steps.
Alert fatigue is a massive business liability. When your internal IT team is buried under thousands of meaningless warnings a day, the single alert that actually signals a catastrophic breach gets ignored.
Escalation Of Validated Findings
Analyst Threat Validation
Clear, Step-By-Step Remediation Playbooks
365 Hardening Plan

360° Attack Surface Visibility
Because modern breaches rarely start on a laptop.
We extend visibility far beyond the endpoint. We monitor Microsoft 365, identities, email activity, DNS, and cloud environments to catch account takeovers and privilege escalations early.
Endpoints (laptops/servers) are just one door. Modern adversaries don't "hack" in anymore. They log in. They hijack your identities, exploit Microsoft 365, and bypass traditional antivirus entirely.
Total Identity And Credential Oversight
Microsoft 365 Compromise Prevention
Rogue Access And Lateral Movement Detection
Impossible Travel Alerts
Layered Containment & Prevention
Alerting is useless without action.
We back detection with containment playbooks and, where your plan includes them, enforcement controls such as application allowlisting and execution restrictions. Under that plan we isolate affected assets and block lateral movement early.
Detection without containment is just an early warning system for a disaster. You don't just need to know an attacker is inside; you need them locked out and isolated quickly so your business operations don't go down.
Automated Compromised Asset Isolation
Lateral Movement Contained
Unapproved Code Blocked From Running

Tactical Response & Escalation
Absolute clarity and command during a crisis.
When a critical threat is validated, we don't just leave you to figure it out. We provide crisis coordination, threat context, and direct response guidance so your leadership and IT teams can contain the threat quickly.
The first hours of an incident shape what it costs. During a crisis, you need experienced responders giving you clear direction, not an automated support ticket.
Executive-Level Crisis Coordination
Exact, Tactical Remediation Guidance
Policy Gap Summary
Runbooks for Automated Defense

Continuous Defense Hardening
Make your defenses stronger over time.
The threat landscape changes daily, and your defense should too. We tune detection rules within the agreed coverage, recommend access-control hardening and flag blind spots, so your security posture improves over time.
Cybersecurity isn't a "set it and forget it" piece of software. As your business scales and attacker tactics change, your defense has to adapt, or it quietly falls behind.
Ongoing Review of Coverage Gaps
Aggressive Detection Rule Tuning
Board-Ready Maturity And Resilience Reporting
24/7 Monitoring and Action
Beyond Monitoring:
The Active Containment Advantage
A true MDR partner doesn't just watch your network and hand you a support ticket when something breaks.
We help you see threats sooner, understand them faster, and, within the authority your response plan grants, cut off an attacker's access early to limit how far an incident spreads.

Live Telemetry Monitoring
We don't wait for batch logs to process. We monitor live telemetry across your endpoints, cloud environments, and identities to catch attackers the second they step out of bounds.

Executive-Level Decision Support
When a crisis hits, you don't need a ticketing portal; you need a war room. We provide exact, tactical direction and escalation support so your internal team knows exactly what to isolate, what to patch, and what to prioritize.

Less Alert Fatigue
We tune out false positives and our analysts investigate alerts from agreed sources, so your team hears about validated threats. We give your IT department time back.

Hardened, Layered Containment
We don't just alert you to a breach. Detection is tied to containment playbooks authorized in your response plan, so we can act early to limit lateral movement.
Beyond Monitoring:
The Active Containment Advantage
Whether you are dealing with an outgunned IT team, struggling to secure Microsoft 365, or facing strict cyber insurance mandates, Cloudskope provides the immediate operational maturity you need to secure your enterprise.
The Ultimate Advantage
A standard IT team is not built to run a security operation. Cloudskope's 24/7 SOC brings experienced threat hunters and tested containment playbooks to your business.
Paired with our specialized Microsoft mastery, we give you an unfair, asymmetric advantage over modern threat actors.
Outgunned Internal IT Teams
Extend your security coverage across nights, weekends, and holidays without the multi-million dollar expense of building, training, and staffing a 24/7 internal SOC.
Securing The Identity Perimeter (M365)
Gain absolute visibility into account takeovers, suspicious sign-ins, and mailbox abuse before attackers can execute a devastating Business Email Compromise (BEC).
Paralyzed by Alert Fatigue
Replace a noisy security stack with analyst-led triage. We investigate the anomalies so your internal team can focus on running the business.
Post-Incident or "Near-Miss" Recovery
Rebuild your defense with confidence. If you have just survived a breach or a near-miss, we close the gaps, harden your environment, and watch for any attempt to get back in.
Cyber Insurance & Compliance Mandates
Satisfy stringent cybersecurity insurance requirements and regulatory compliance mandates (like NIST, HIPAA, or CMMC) that increasingly demand 24/7 active threat monitoring and incident response.
Board-Level Reporting
Skip the three-year IT roadmap. Achieve enterprise-grade detection, containment, and resilience on day one without the massive internal hiring overhead.

Frequently Asked Questions
Answers to the most common questions about scope, process, and what happens after the audit.
Start With a Scoping Call
Buying more security dashboards will not stop a determined attacker. A scoping call covers your environment, what we would monitor, who holds containment authority and how escalation works, so you know exactly what coverage looks like before you commit.