

Blog Tag
Executive Cyber Risk
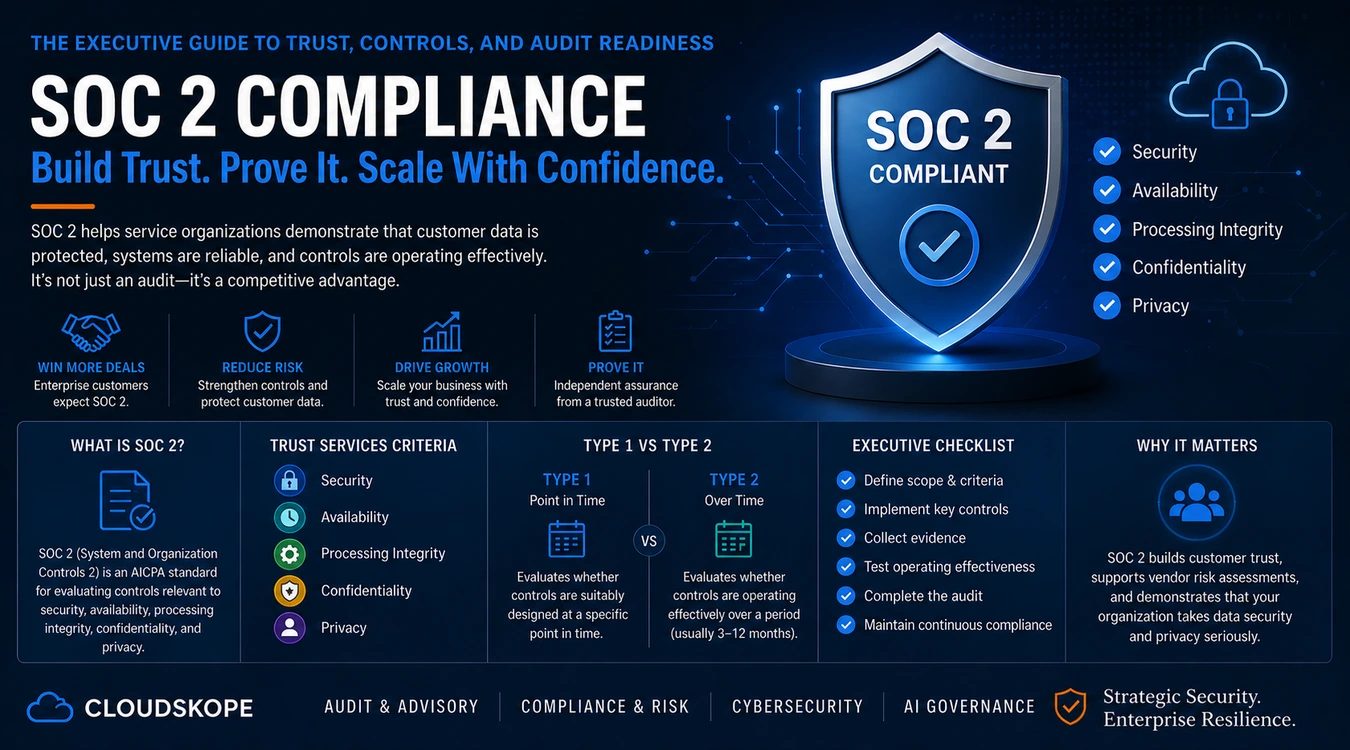


What Is SOC 2 Compliance? An Executive Guide
SOC 2 for executives: what auditors test, what consultants charge, what boards need to know — and why Type II is what enterprise buyers require.
Best Practices
When the Security Tool Becomes the Attack Surface
When the security tool becomes the attack surface: the Microsoft Defender exploit chain, the SentinelOne kernel CVE, and the pattern now common across EDR.
Best Practices