

Security Blog
Expert insights, threat intelligence, and best practices from our security team

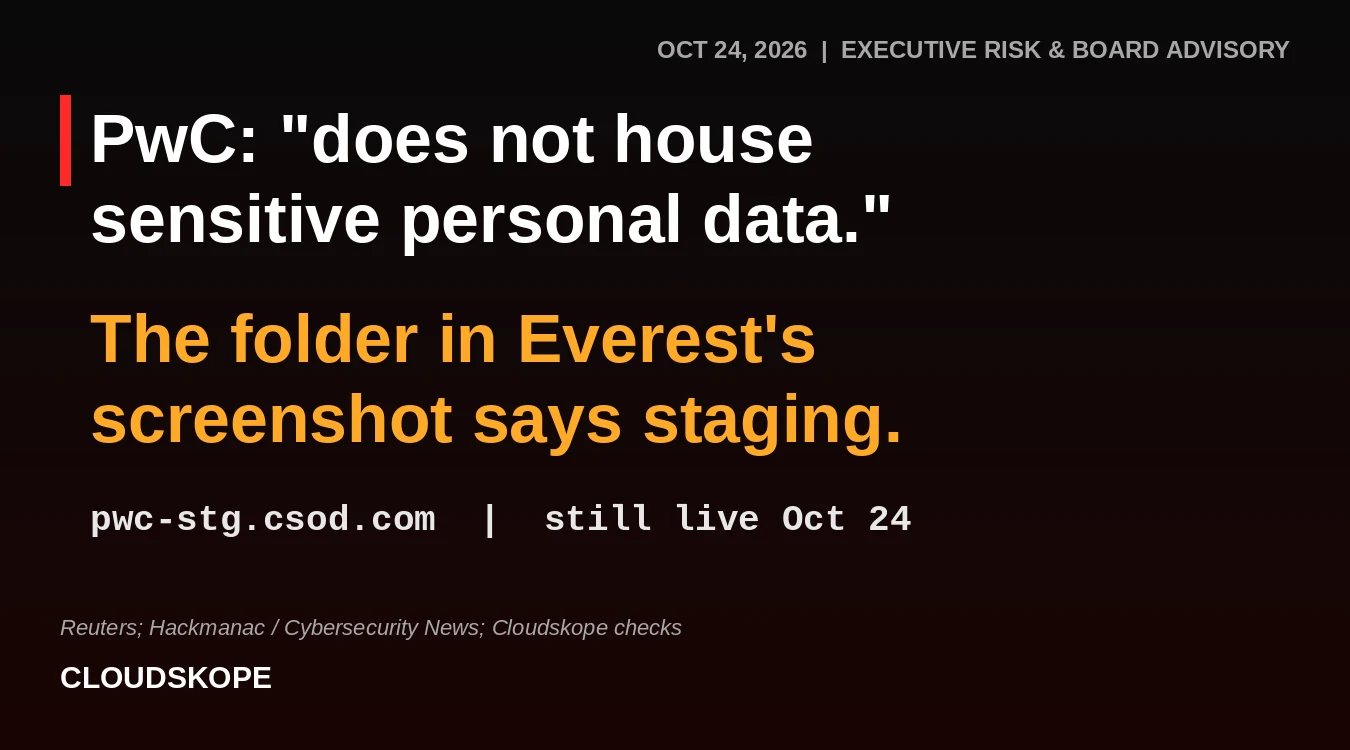


PwC Won't Name the Vendor. Everest's Screenshot Does. It Says Staging.
PwC confirmed a vendor incident but won't name the vendor. Everest's screenshot points to a live Cornerstone staging tenant. What it means for PwC's clients.
Executive Risk & Board Advisory
Latest Articles
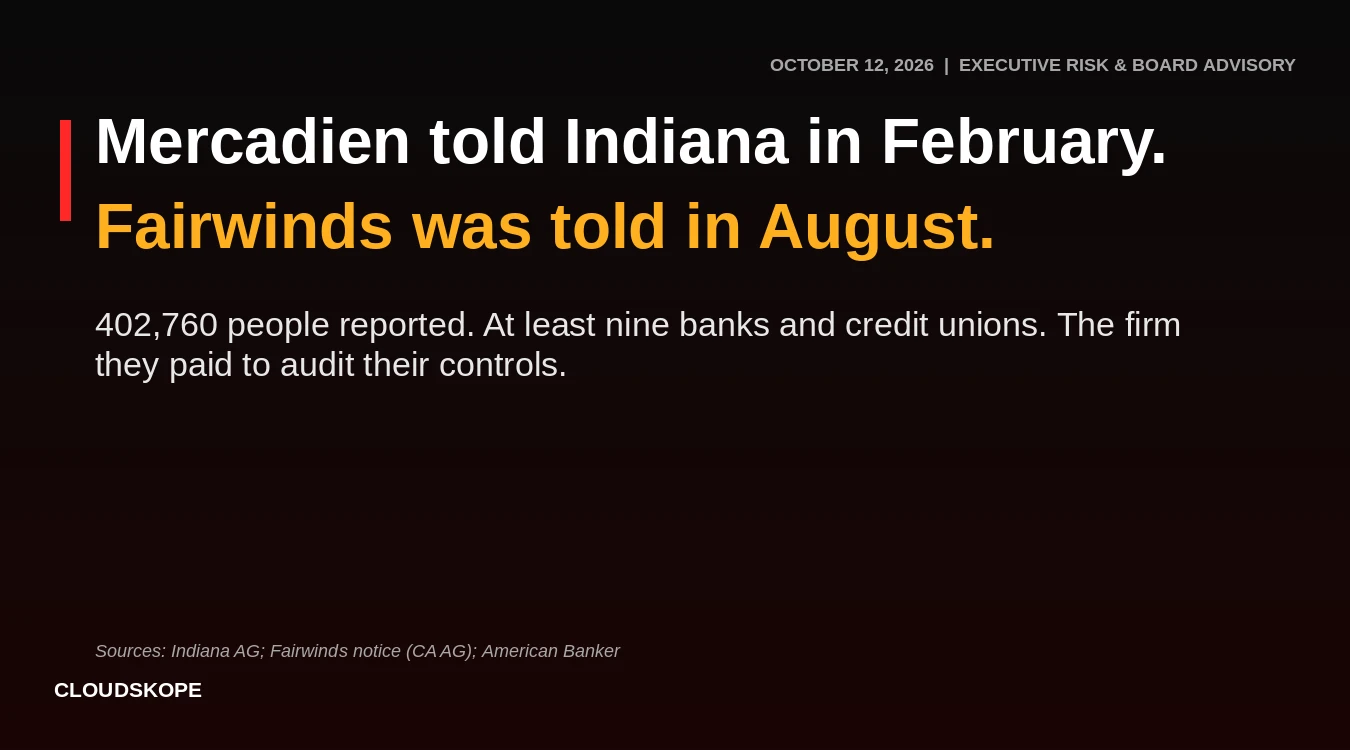
402,760 People. Nine Banks and Credit Unions. Mercadien Told Indiana in February and Fairwinds in August.
A bank auditor's breach reached at least nine banks and credit unions. Mercadien filed a count in February. Some clients were told 279 days after discovery.
Executive Risk & Board Advisory
Law Firms Are the Names in the Ledger. Deal Data Is the Product.
Silent Ransom Group's leaked ledger tallies $207M from 27 paid victims. Its targets are mostly law firms; the FBI warned them in 2025. Next: accounting, insurance, finance.
Executive Risk & Board Advisory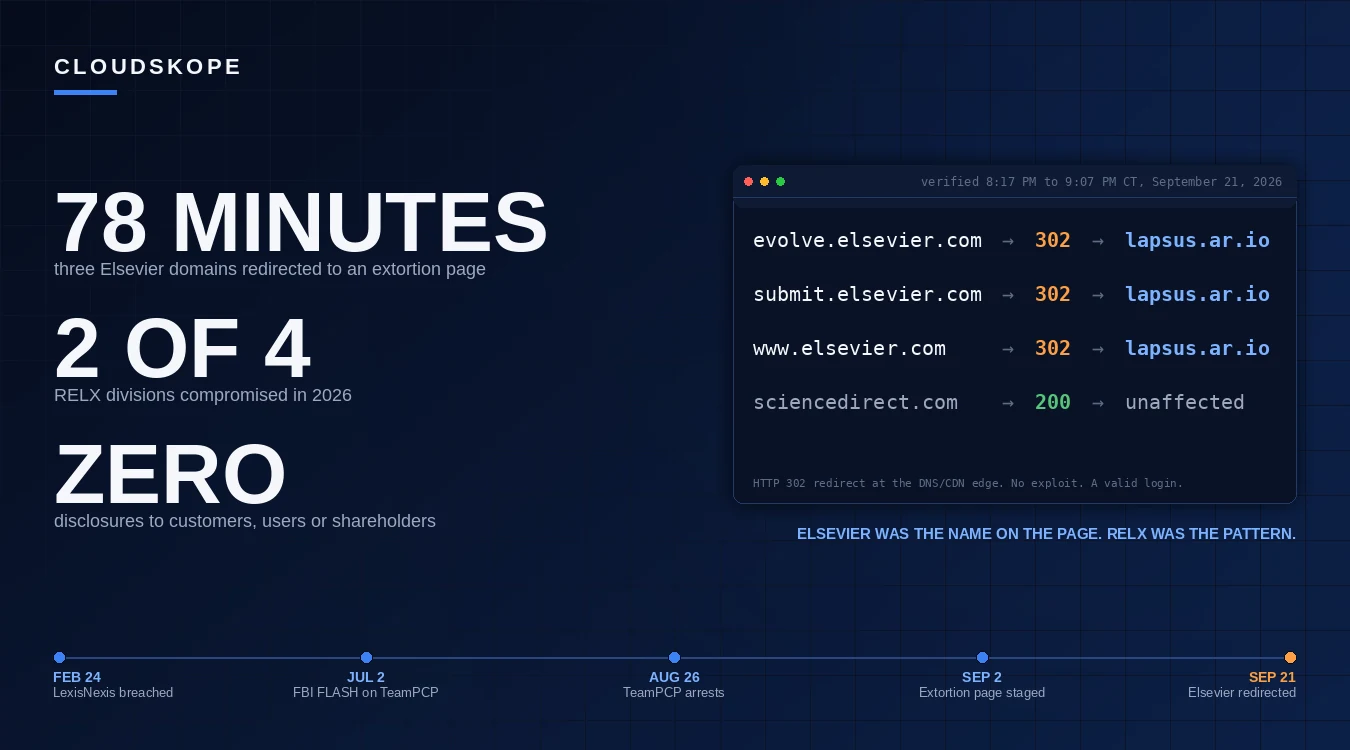
Elsevier Was the Name on the Page. RELX Was the Pattern.
The page was staged Sept 2. The FBI named the credentials in July. LexisNexis, Elsevier's sister company, was breached by the same network in February. RELX has disclosed none of it.
Executive Risk & Board Advisory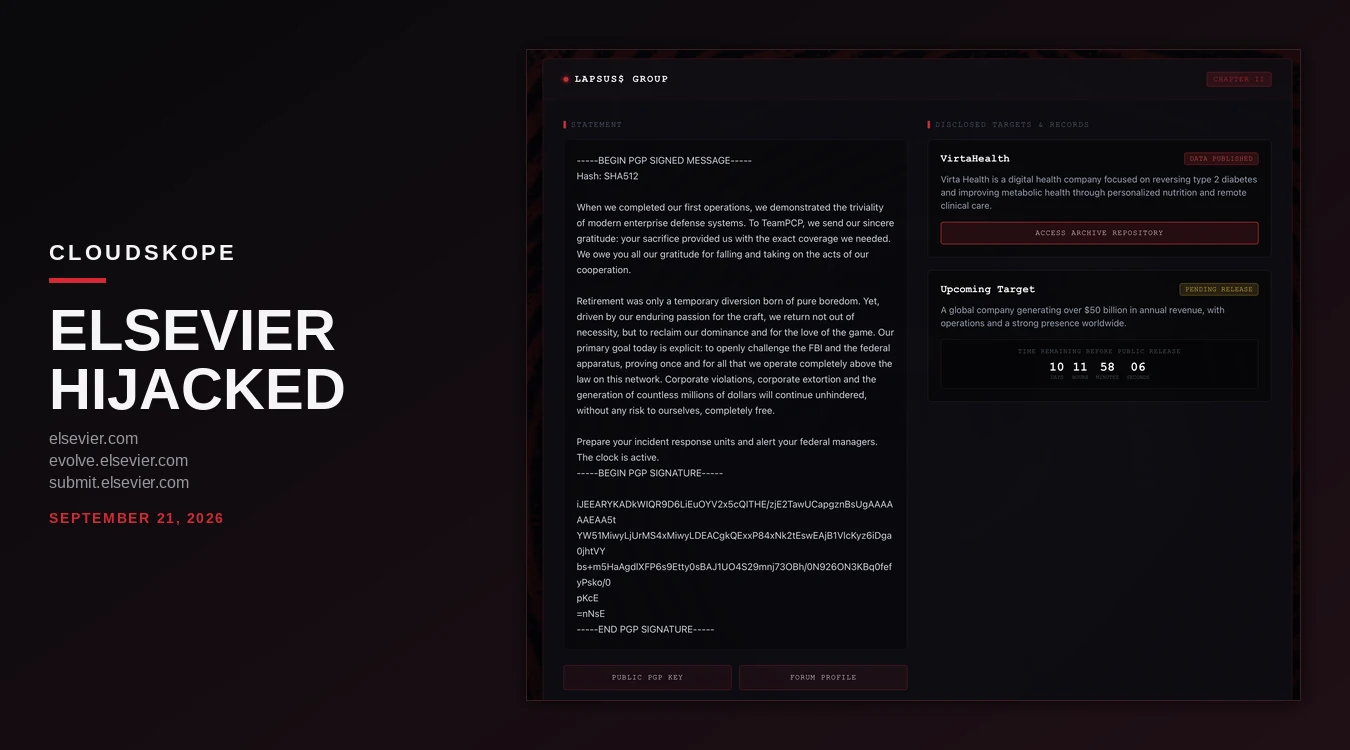
Is Sherpath Hacked? What Happened to Evolve and Elsevier on September 21
Evolve, the sign-in door for Sherpath and HESI, redirected to an extortion page for about two hours on Sept 21. What happened, and what to do if you signed in.
Executive Risk & Board Advisory
Nutex Health Filed Under 8.01. Seven Days Later It Filed Under 1.05. The Class Action Landed in Between.
Nutex Health filed a cyber incident under SEC Item 8.01, then converted to Item 1.05 seven days later. A class action arrived in between. What the sequence means for boards.
Executive Risk & Board Advisory
Fifteen Months, One Phone Call: How the Same Attack Went From Marks & Spencer to Apollo Global Management
The same attack technique ran from UK retail in April 2025 to Wall Street in July 2026. Fifteen months, public the entire time, and the controls that stop it are neither new nor expensive.
Executive Risk & Board Advisory
How a Phone Call Beats MFA: Anatomy of the Wall Street Vishing Wave
Anatomy of the vishing wave hitting Wall Street: how a phone call captures the authenticated session MFA produces, the indicators to hunt for, and the controls that close the exposure.
Executive Risk & Board Advisory
Apollo. Blackstone. Bridgewater. Bain. The Same Crew Is Vishing Them All — And Bain Is Already a Defendant.
Apollo, Blackstone, Bridgewater, and Bain Capital are all in the crosshairs of the same vishing campaign. Bain is already a defendant in the first sponsor-liability ruling. Two-front war on PE.
Executive Risk & Board Advisory
Take-Two Lost $2.8 Billion. The Hacker Cashed Out $250,000. Nobody Ever Sent a Ransom Note.
CyberLeek leaked GTA VI, pumped a memecoin, and cashed out $250K without ever demanding a ransom. What the first market-monetized extortion means for boards and deal teams.
Executive Risk & Board Advisory
Three Breaches, Three Years. Client Tax Records in a Hacker's Hands. EY Still Won't Name the Platform That Failed.
EY was breached a third time in three years, and this time the stolen files are client tax records. What boards and PE deal teams should be asking now.
Executive Risk & Board Advisory
Amazon's One Medical Confirms a "Limited" Breach. ShinyHunters Claims 8.8 Terabytes and a Deadline. Only One of Those Is Verified.
On June 13, One Medical disclosed unauthorized access to a third-party file storage system holding archived records from its legacy Iora Health and One Medical Seniors patients, describing the scope as a limited subset of files at nine named clinics. Days earlier, on June 18, ShinyHunters posted One Medical to its dark-web leak site, claimed 8.8 terabytes of stolen data, and gave the company until June 22 to begin negotiating before publication. ShinyHunters has released no sample data, so the claim is unverified. This is the same actor, the same playbook, and the same trust gap Cloudskope documented in the Canvas/Instructure breach: a company describing the smallest defensible version of events while a threat actor describes the largest. For boards in healthcare and any regulated-data business, the lesson is not which number to believe. It is to treat both as unproven until the evidence settles it, and to plan for the larger one.
Executive Risk & Board Advisory
Drift. Gainsight. Now Klue. And This Time, It Wasn't ShinyHunters.
For the third time in ten months, attackers drained Salesforce data through a trusted app. The first two were ShinyHunters. This one wasn’t — and that is why it matters.
Executive Risk & Board Advisory
Operation Epic Fury. Volt Typhoon. BRICS Settlement Rails. Your Portfolio's Cyber Risk Just Became a Geopolitical Position.
The convergence of Operation Epic Fury, Volt Typhoon's pre-positioned access inside US infrastructure, and BRICS de-dollarization is not a geopolitics story. It is a portfolio risk story. Ray Dalio calls this Stage 6 of the Big Cycle — the restructuring phase, where debt-laden empires compete through proxies and economic warfare rather than direct confrontation. Paul Kennedy called the underlying dynamic "imperial overstretch." Jared Diamond would note the resource pressure and institutional fragility. Thomas Friedman would observe that the world is no longer flat. For PE deal teams and portfolio operators, the relevant question is not who wins the geopolitical contest. It is which of your portcos are inside the blast radius of a conflict none of them signed up for.
Executive Risk & Board Advisory
Five Cyber Questions That Change What a Deal Is Worth.
Cyber due diligence is usually a checkbox near the end of the process. Five specific questions turn it into a deal-pricing input, surfacing the risks that actually move valuation and post-close cost.
Executive Risk & Board Advisory
Acquisition Agreements Get Signed on Cyber Reps Nobody Verified. That Becomes the GC's Problem.
Acquisition agreements get signed on cyber reps no one independently verified. When the deal closes, the gap between what was repped and what's true becomes the buyer's liability and the GC's problem. What deal counsel should require first.
Executive Risk & Board Advisory
The First 100 Days After Close Decide Your Cyber Risk for the Whole Hold.
Cyber due diligence is a screen, not a clean bill of health. The day a deal closes, every undetected weakness becomes the sponsor's problem, and the first 100 days are the only window with the leverage to fix it.
Executive Risk & Board Advisory
Your Cyber Budget Is a Number. Your Cyber Risk Is a Distribution. CFOs Keep Confusing the Two.
Global cyber spending hit a record $219 billion in 2025, the same year breaches set their own record. The disconnect exposes the core CFO error: treating cybersecurity as a budget number instead of a loss distribution to reshape.
Executive Risk & Board Advisory
Four Breaches in Six Weeks. One Extortion Group. Your Portfolio Is the Target List.
ShinyHunters spent early 2026 running one pay-or-leak campaign through Instructure, Adobe, Match Group, and DentaQuest. The target profile is a near-perfect description of the average PE portfolio company.
Executive Risk & Board Advisory
What CISA's CI Fortify Guidance Actually Means, and Why It Reads Like a Confession
CISA's CI Fortify guidance tells critical infrastructure to plan for months running cut off from its own networks, on the assumption the adversary is already inside. Why that reads like a confession.
Executive Risk & Board Advisory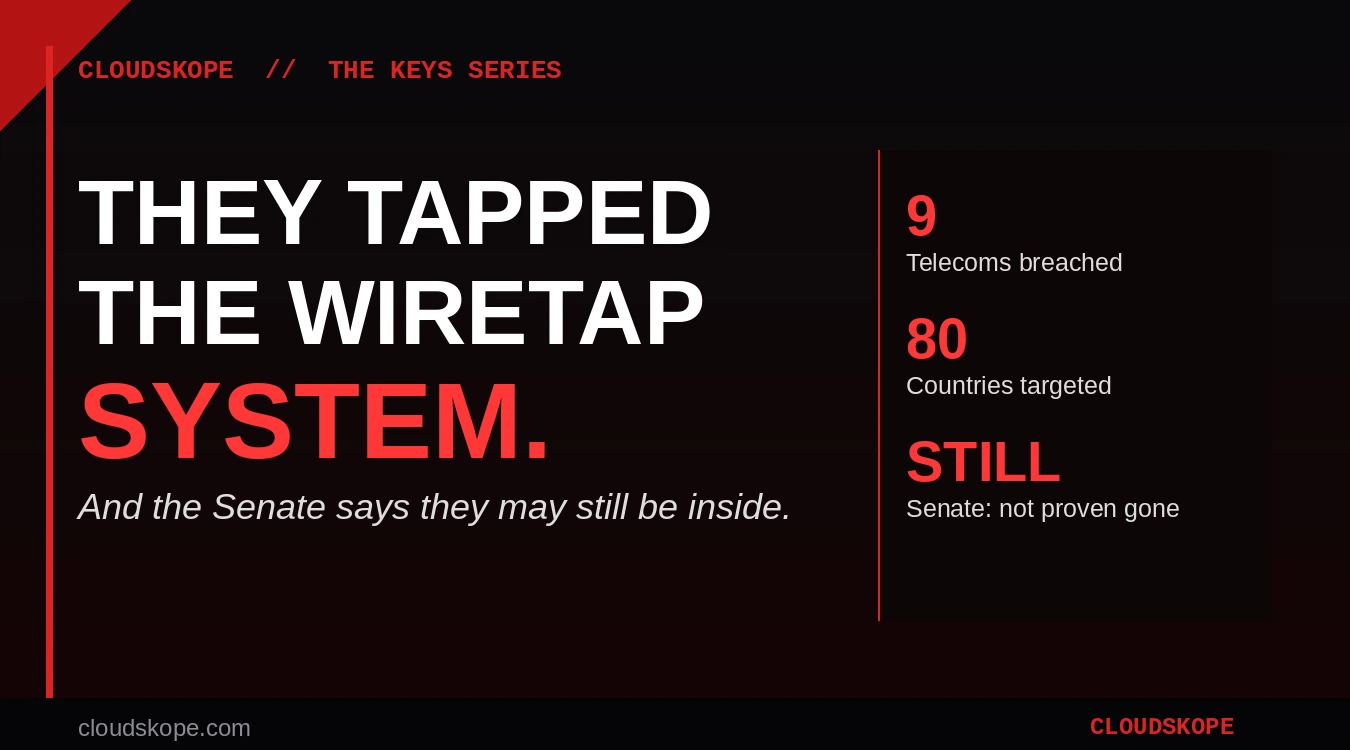
Still Inside: Why the Senate Says Salt Typhoon Was Never Fully Evicted
Salt Typhoon breached at least nine US carriers and the wiretap systems built for law enforcement. The Senate now says China's hackers were never fully evicted.
Executive Risk & Board Advisory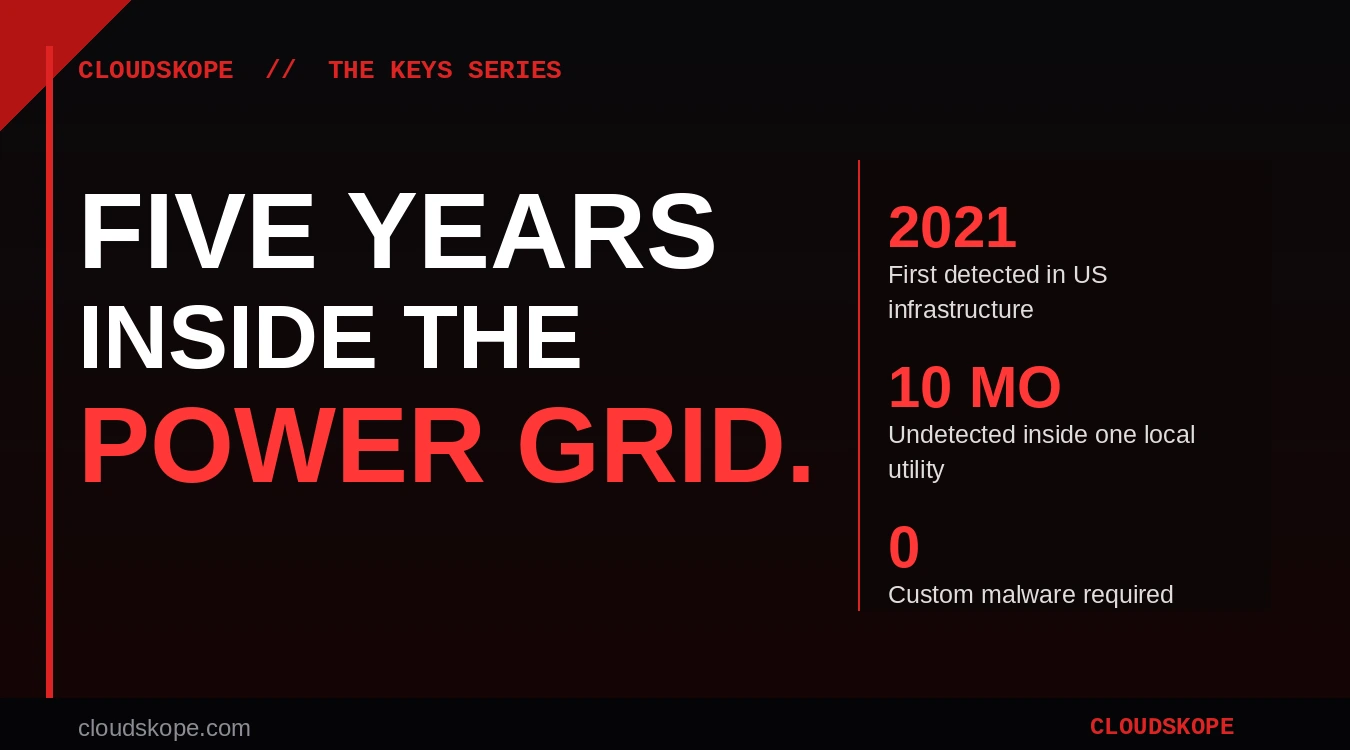
Seven Years Inside: What Volt Typhoon Is Actually Doing in the US Power Grid
China's Volt Typhoon has held access inside US critical infrastructure for roughly seven years, using no malware. The goal isn't espionage. It's pre-positioning for disruption.
Executive Risk & Board Advisory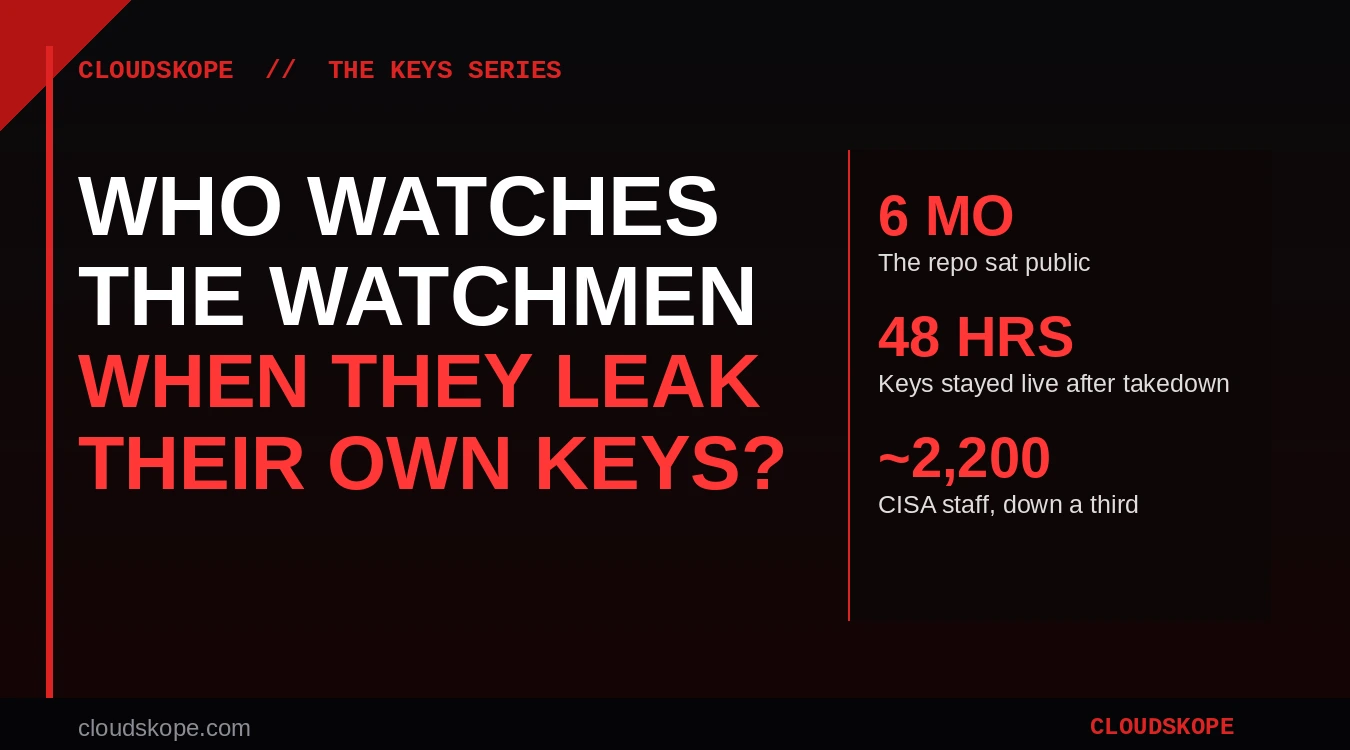
Nine Days After CISA Told America to Lock Down, Its Own Keys Were Sitting on GitHub
Days after CISA told America to lock down, a CISA contractor's public GitHub repo exposed federal cloud keys and the agency's software build credentials for six months.
Executive Risk & Board Advisory
AT&T Holds the Keys to Federal Surveillance. A Whistleblower Says It Hid the Break-Ins.
A whistleblower suit alleges IBM and AT&T hid repeated Chinese intrusions into a federal cloud system and made false security assurances to keep their government contracts.
Executive Risk & Board Advisory
Five Warnings in Sixty Days: The Keys to America's Infrastructure Are Not Being Held
Five infrastructure-security stories broke in sixty days, each reported alone. Read together, they say the keys to America's critical systems are not being held.
Executive Risk & Board Advisory
The West Is Not Losing a Cyberwar. It's Losing an Economic War Conducted Through Cyber Means.
GCHQ's director warns of a 'narrowing window' while Russia hits Europe daily and China sits inside US telecoms. This isn't a cyberwar; it's economic coercion through digital infrastructure.
Executive Risk & Board Advisory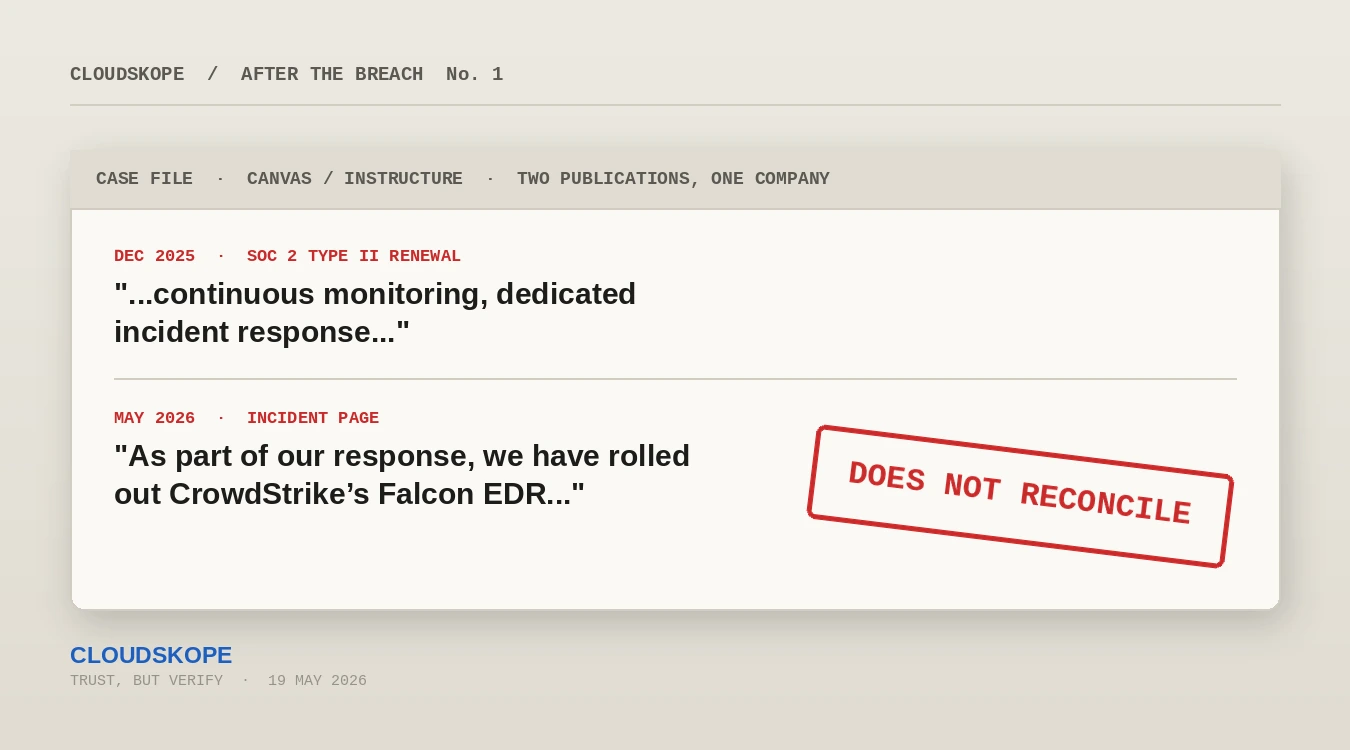
Instructure's Own Documents Don't Add Up
A document-by-document reconstruction of the Canvas/Instructure breach, where the company's own SOC 2 renewal, incident page, and containment claims do not reconcile with what it later admitted.
Executive Risk & Board Advisory
Instructure Paid Off Its Hackers. The House Homeland Security Committee Wants to Know Why.
On May 12, 2026, Instructure announced a settlement with the ShinyHunters criminal organization that breached its Canvas platform, claiming that all stolen data has been "returned" and that the threat actor has provided "digital confirmation of data destruction." The same day, the House Homeland Security Committee sent a letter to Instructure CEO Steve Daly requesting a briefing on the breach response and on the adequacy of coordination with federal law enforcement and CISA. A settlement is not a resolution. A promise from criminals is not a defensive posture. The pattern of conduct that produced three breaches in eight months has not been addressed. The students at 8,809 schools whose data was taken were not parties to the agreement that supposedly now protects them.
Executive Risk & Board Advisory
Phishing Statistics 2026: 20 Numbers Every Executive Should Know
20 phishing statistics from Verizon DBIR, IBM, FBI IC3, APWG, Microsoft, and Proofpoint that should change how every executive thinks about email security investment in 2026.
Executive Risk & Board Advisory
Audited. Compliant. Hacked Anyway.
$219 billion spent on cybersecurity in 2025. More major breaches than any year on record. Why every cybersecurity plan failed in 2026.
Executive Risk & Board Advisory
Most Common Passwords in 2026: What the Data Shows
The 2026 password data: 123456 is still #1, 65% of users reuse passwords across breaches. What boards and CISOs should be doing about it.
Executive Risk & Board Advisory
Cybersecurity Acronyms Glossary 2026
70+ cybersecurity acronyms decoded for executives, boards, and PE sponsors. MFA, EDR, MDR, ZTNA, NIST CSF, SOC 2, and the rest — organized across 11 categories.
Executive Risk & Board Advisory
30 Biggest Data Breaches of All Time
Ranked by records: Yahoo, NPD, LinkedIn, Marriott, Canvas, T-Mobile, Equifax, Target, Capital One, Change Healthcare — and the regulatory fallout each produced.
Threat Intelligence
Seven Years. Five Wells Fargo Outages. Still 'Routine.'
Seven years. Five major outages. Wells Fargo still calls it routine maintenance. What the banking outage pattern reveals about regulated comms.
Executive Risk & Board Advisory
275M Users Exposed in Canvas/Instructure Breach
275 million users exposed. 8,809 schools down. Instructure calls it 'scheduled maintenance.' Inside the Canvas breach and the EdTech disclosure failure.
Executive Risk & Board Advisory
Scattered Spider Plea: The Playbook Is Now Commoditized
Scattered Spider operative 'TylerB' pleaded guilty. The real threat isn't the arrest — it's that the social engineering playbook is now commoditized.
Executive Risk & Board Advisory
Shadow AI Agents Are Your New Attack Surface
Employees are running unauthorized AI agents with admin access to email, files, calendars, and CRM. The shadow AI attack surface most enterprises don't measure.
AI Governance
Microsoft Edge Stored Every Password in Cleartext
Microsoft Edge has been storing saved passwords in cleartext on disk. Any process with disk access can read them. What it means for enterprise password hygiene.
Microsoft 365 & Azure
Russia Harvested 18,000+ M365 Tokens Without Malware
Russia harvested 18,000+ Microsoft 365 OAuth tokens through compromised home routers — no malware, no detectable footprint. Inside the campaign.
Threat Intelligence
Every MFA Tool Is Being Bypassed. Here's How.
Every MFA tool in your stack is being bypassed right now. Adversary-in-the-middle phishing, SIM swap, MFA fatigue, push bombing — and what actually stops them.
Identity & Access
Defender vs CrowdStrike vs SentinelOne: 2026 Test
We tested Microsoft Defender, CrowdStrike Falcon, and SentinelOne against identical threats. The results were not what most CISOs expect.
Remediate & Protect
April's 167 CVEs Were a Governance Failure
April Patch Tuesday shipped 167 CVEs with 14 critical exploitable bugs. The problem isn't patching capacity — it's the governance framework deciding priority.
Threat Intelligence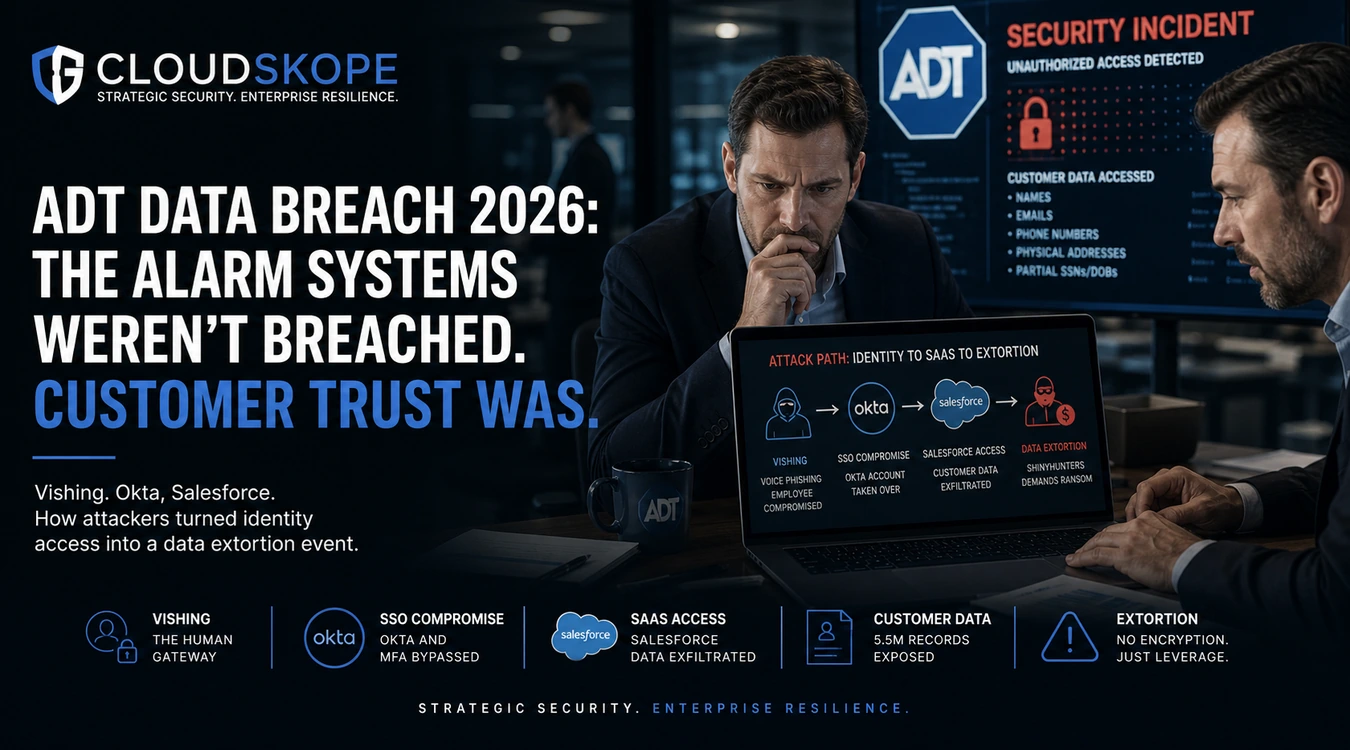
ADT 2026 Breach: Customer Trust Was the Breach
The ADT 2026 breach didn't compromise the alarm systems. It compromised the customer data underneath — and the vishing campaign that followed showed the real risk.
Threat Intelligence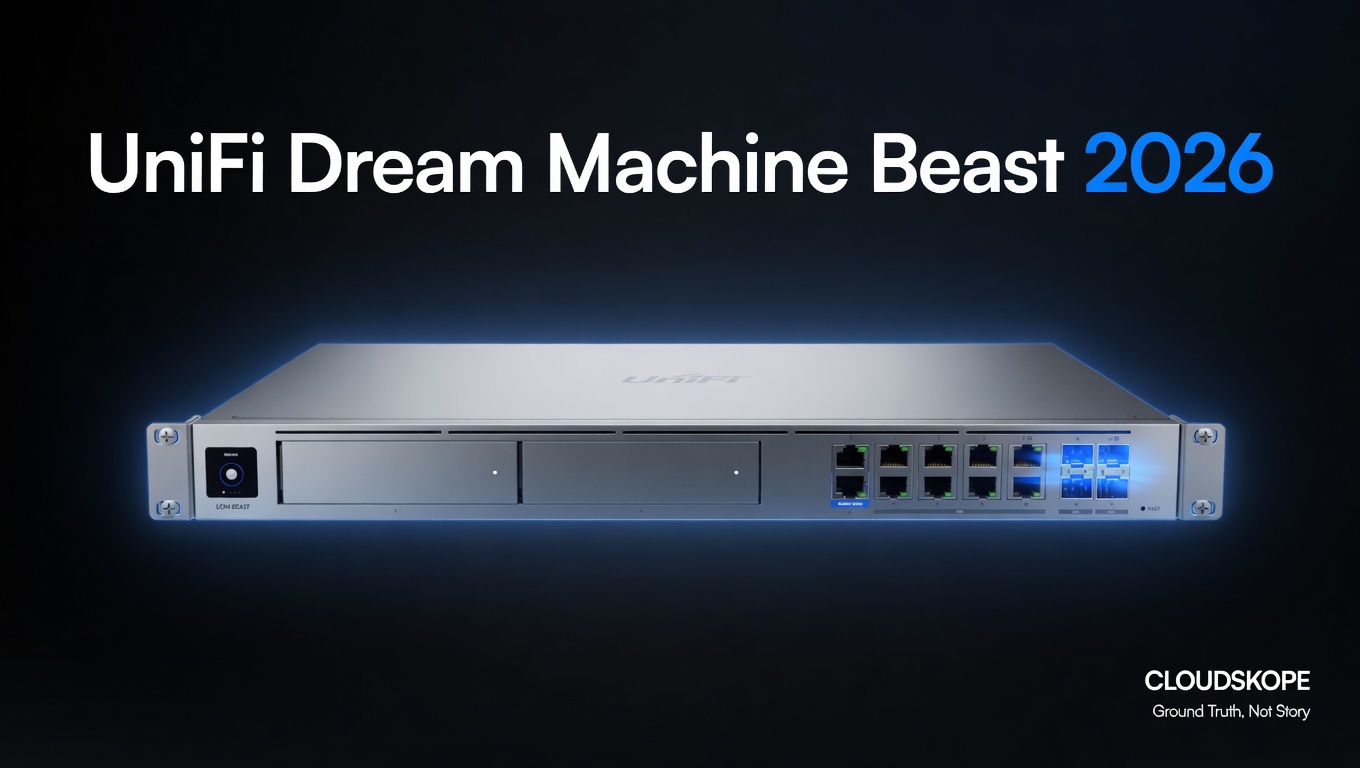
UniFi Dream Machine Beast: Enterprise Push
Ubiquiti's Dream Machine Beast pushes UniFi into enterprise gateway territory. Technical specs, threat-model implications, and mid-market network fit.
Automation & Infrastructure
White House Correspondents' Dinner: Perimeter Failure
The White House Correspondents' Dinner breach: insider risk, badge cloning, and the slow failure of trust-by-credential perimeter models.
Executive Risk & Board Advisory
Copilot Doesn't Create the Data Problem. It Reveals It.
Microsoft 365 Copilot does not create a permission problem. It reveals the one you already had. Inside the SharePoint sprawl Copilot exposes.
Executive Risk & Board Advisory
The Uncomfortable Truth About AI Threat Detection
AI threat detection vendors promise what their products can't deliver. Pattern matching is not detection — and most stacks are catching less than claimed.
Best Practices
Frost Bank and the New Vendor-Risk Reality
The Frost Bank vendor breach: what happens when a payment processor's third-party software fails. The vendor-risk reality boards and audit committees own.
Compliance
Flat Networks Turn Incidents Into Enterprise Events
Flat networks turn small incidents into enterprise events. The segmentation framework that limits blast radius — and why mid-market still hasn't done it.
Best Practices
Ransomware Trends: Q2 2026 Analysis
Q2 2026 ransomware analysis: the operator economics, targeted sectors, cryptocurrency flow, and regulatory responses now reshaping breach disclosure practice.
Compliance
AI Tools With Company Keys: The Vercel Breach
When AI tools get the keys to your company: the Vercel breach exposed the API credentials AI agents need to function — and how attackers chained that access.
Best Practices
Network Gear Is the Attack Surface Nobody Audits
Your network gear is becoming the attack surface nobody audits enough. Firewalls, switches, load balancers, and the CVE backlog hiding in your perimeter.
Compliance
Patch Tuesday Is a Governance Test
Patch Tuesday is not an IT task — it is a governance test. The 30-day patching SLA, board reporting, and named-officer accountability framework boards now own.
Threat Intelligence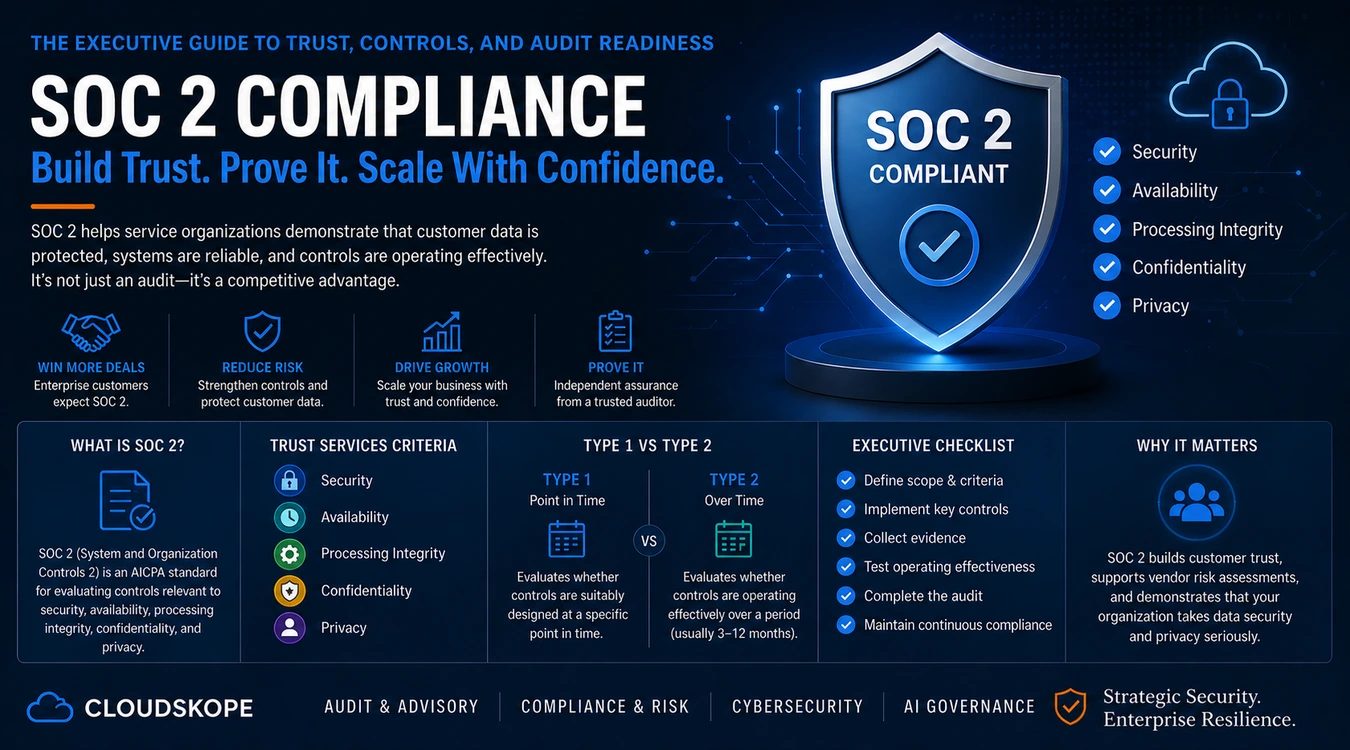
What Is SOC 2 Compliance? An Executive Guide
SOC 2 for executives: what auditors test, what consultants charge, what boards need to know — and why Type II is what enterprise buyers require.
Best Practices
When the Security Tool Becomes the Attack Surface
When the security tool becomes the attack surface: the Microsoft Defender exploit chain, the SentinelOne kernel CVE, and the pattern now common across EDR.
Best Practices