

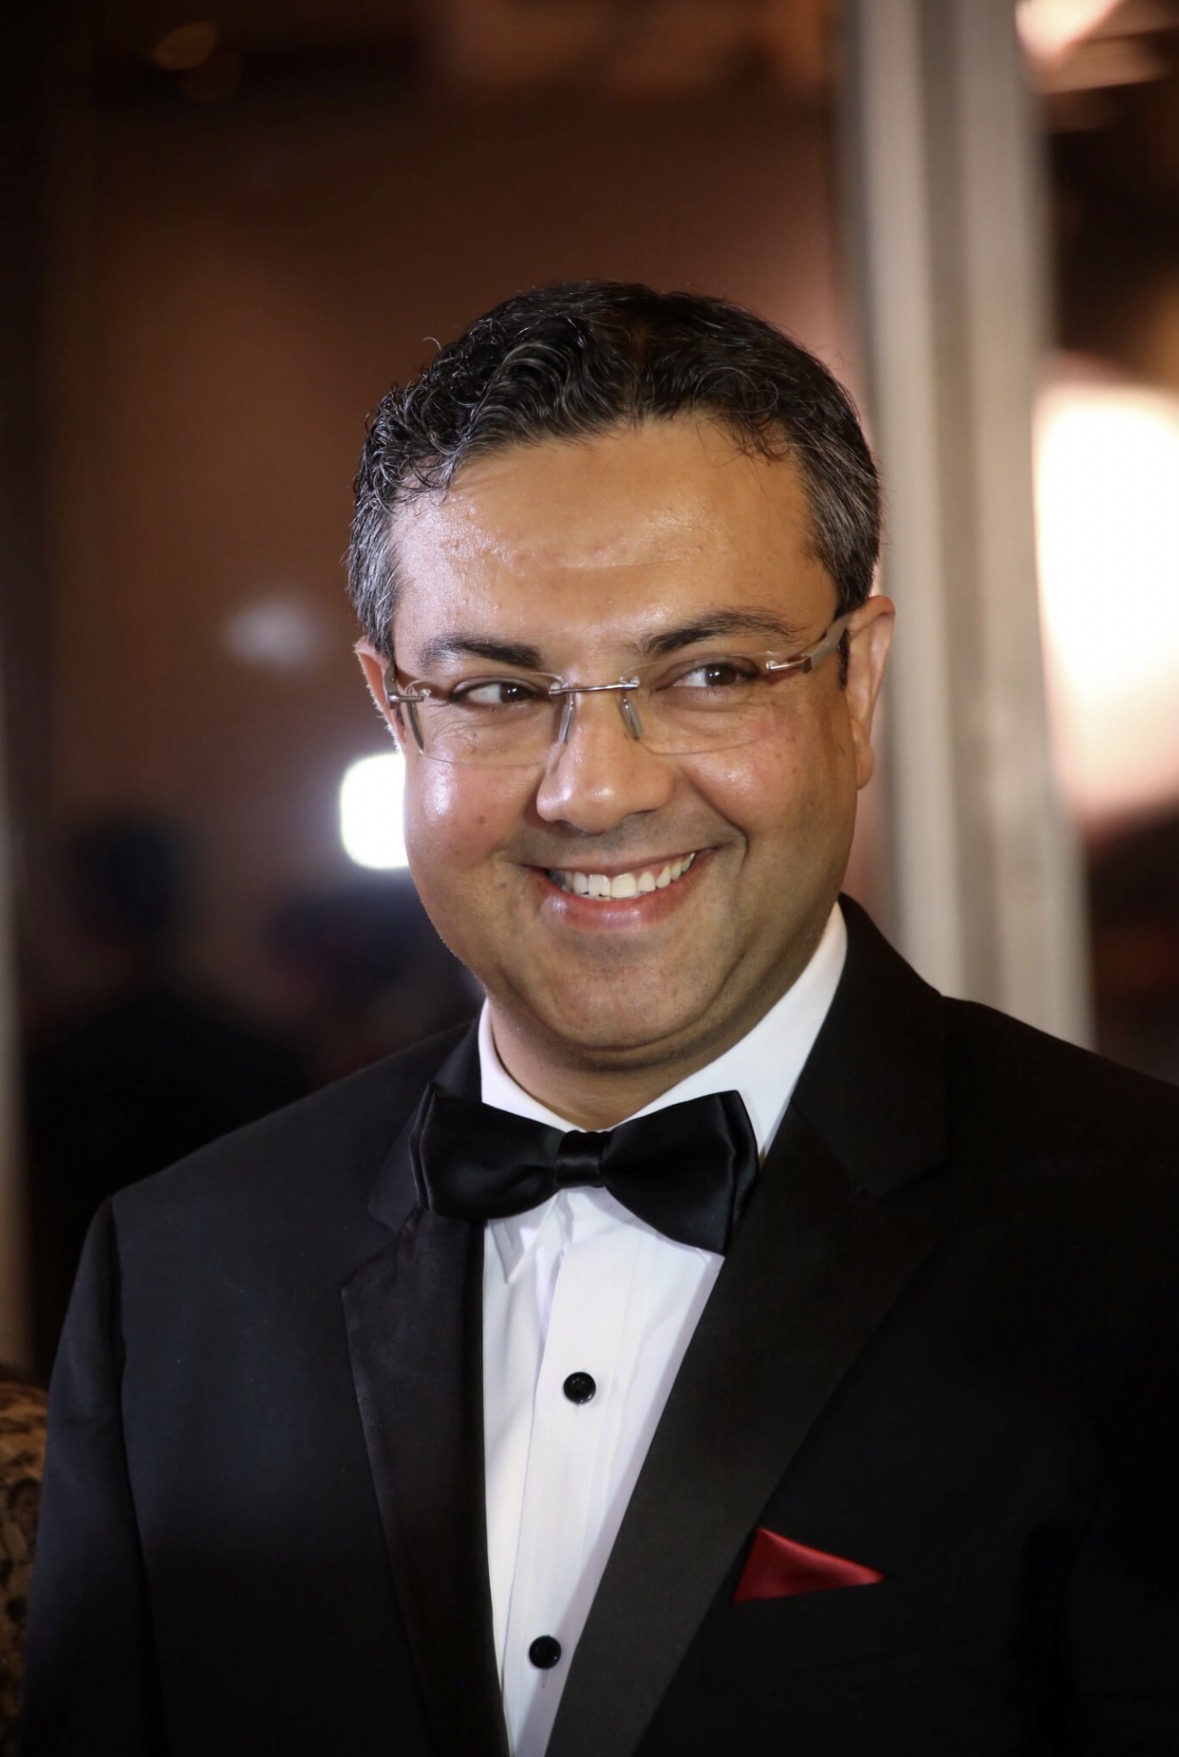
Dipan Mann
Founder, CEO & CTO
Dipan Mann is the founder and CEO of Cloudskope, an elite cybersecurity consulting firm that works with private equity sponsors, portfolio companies, boards, CFOs, and general counsel.
He began his career in the public sector. Before founding Cloudskope he held senior technology and customer experience leadership roles at LogicMonitor and LiveVox. He serves on the board of The Channel Company.
He writes most of what appears on this site: breach analysis, M&A cyber due diligence, and the questions boards should be asking before a deal closes rather than after. The recurring subject is the distance between assumed security and actual security, and who is holding the liability when the two turn out to be different.
Cloudskope is headquartered in Dallas and works with clients nationally. Connect on LinkedIn.


AI Tools With Company Keys: The Vercel Breach
When AI tools get the keys to your company: the Vercel breach exposed the API credentials AI agents need to function — and how attackers chained that access.
Best Practices

Network Gear Is the Attack Surface Nobody Audits
Your network gear is becoming the attack surface nobody audits enough. Firewalls, switches, load balancers, and the CVE backlog hiding in your perimeter.
Compliance
Patch Tuesday Is a Governance Test
Patch Tuesday is not an IT task — it is a governance test. The 30-day patching SLA, board reporting, and named-officer accountability framework boards now own.
Threat Intelligence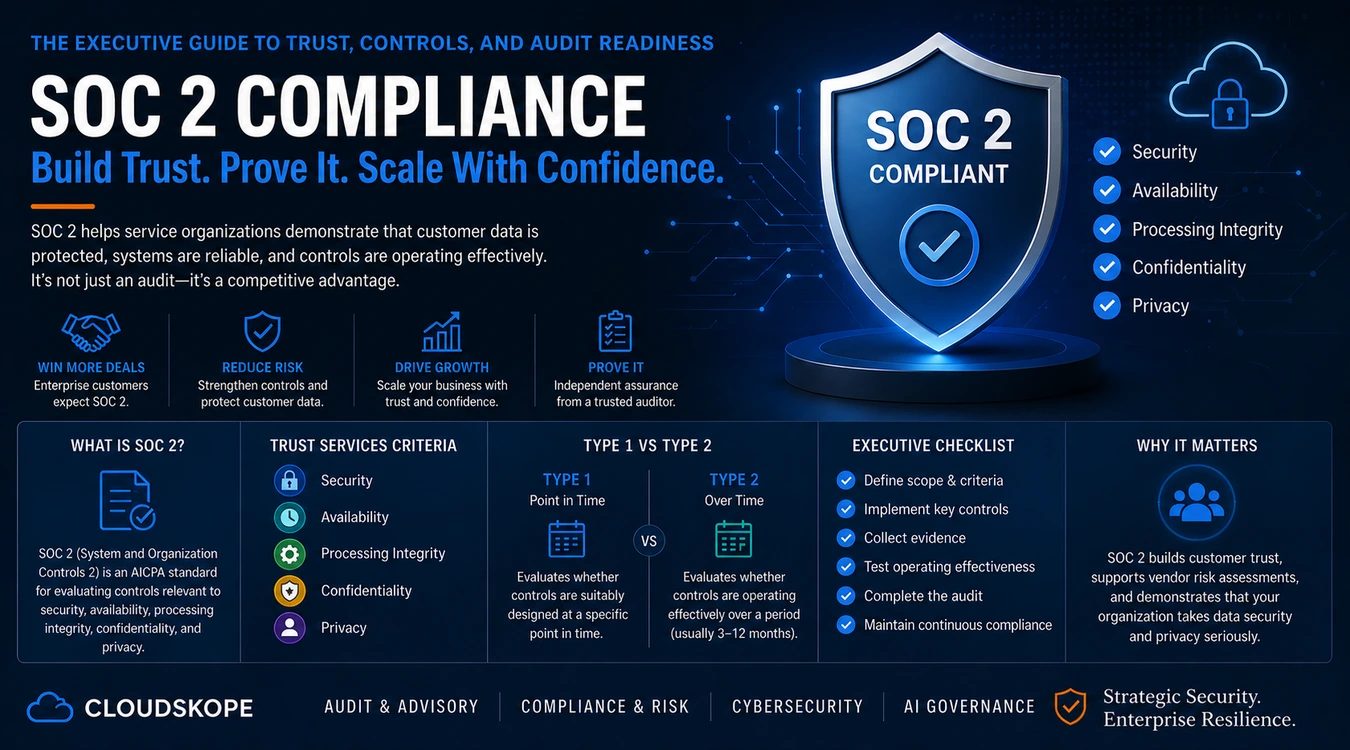
What Is SOC 2 Compliance? An Executive Guide
SOC 2 for executives: what auditors test, what consultants charge, what boards need to know — and why Type II is what enterprise buyers require.
Best Practices
When the Security Tool Becomes the Attack Surface
When the security tool becomes the attack surface: the Microsoft Defender exploit chain, the SentinelOne kernel CVE, and the pattern now common across EDR.
Best Practices