

Dipan Mann
Founder, CEO & CTO
Dipan Mann is the founder and CEO of Cloudskope, an elite cybersecurity consulting firm that works with private equity sponsors, portfolio companies, boards, CFOs, and general counsel.
He began his career in the public sector. Before founding Cloudskope he held senior technology and customer experience leadership roles at LogicMonitor and LiveVox. He serves on the board of The Channel Company.
He writes most of what appears on this site: breach analysis, M&A cyber due diligence, and the questions boards should be asking before a deal closes rather than after. The recurring subject is the distance between assumed security and actual security, and who is holding the liability when the two turn out to be different.
Cloudskope is headquartered in Dallas and works with clients nationally. Connect on LinkedIn.
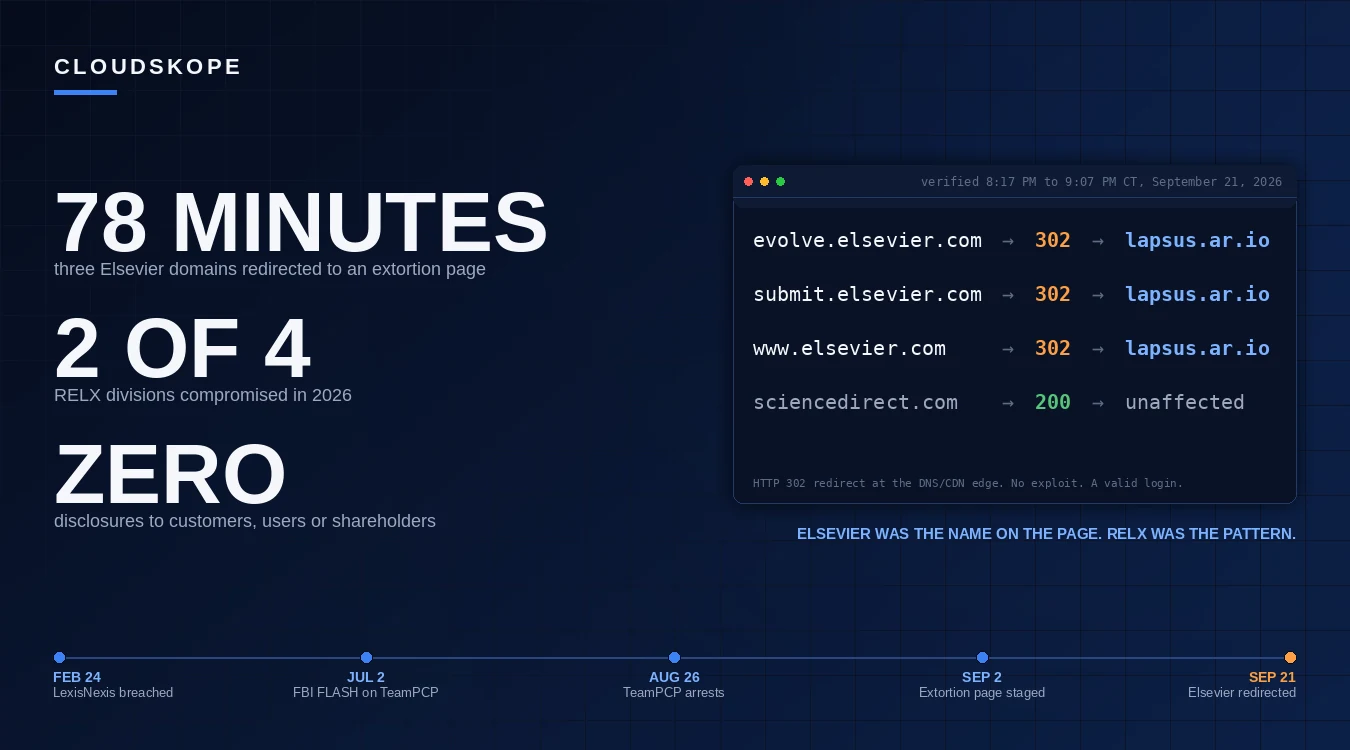


Elsevier Was the Name on the Page. RELX Was the Pattern.
The page was staged Sept 2. The FBI named the credentials in July. LexisNexis, Elsevier's sister company, was breached by the same network in February. RELX has disclosed none of it.
Executive Risk & Board Advisory
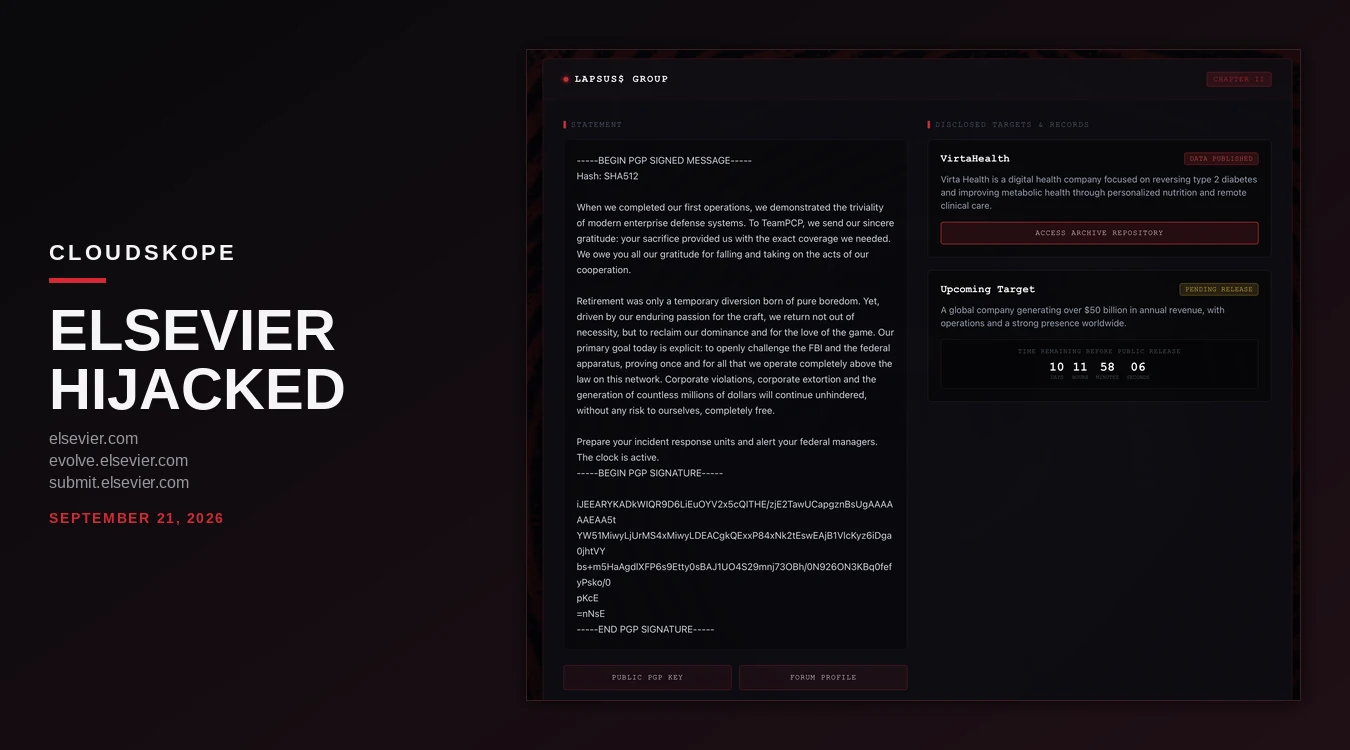
Is Sherpath Hacked? What Happened to Evolve and Elsevier on September 21
Evolve, the sign-in door for Sherpath and HESI, redirected to an extortion page for about two hours on Sept 21. What happened, and what to do if you signed in.
Executive Risk & Board Advisory
Nutex Health Filed Under 8.01. Seven Days Later It Filed Under 1.05. The Class Action Landed in Between.
Nutex Health filed a cyber incident under SEC Item 8.01, then converted to Item 1.05 seven days later. A class action arrived in between. What the sequence means for boards.
Executive Risk & Board Advisory
Fifteen Months, One Phone Call: How the Same Attack Went From Marks & Spencer to Apollo Global Management
The same attack technique ran from UK retail in April 2025 to Wall Street in July 2026. Fifteen months, public the entire time, and the controls that stop it are neither new nor expensive.
Executive Risk & Board Advisory
How a Phone Call Beats MFA: Anatomy of the Wall Street Vishing Wave
Anatomy of the vishing wave hitting Wall Street: how a phone call captures the authenticated session MFA produces, the indicators to hunt for, and the controls that close the exposure.
Executive Risk & Board Advisory
Apollo. Blackstone. Bridgewater. Bain. The Same Crew Is Vishing Them All — And Bain Is Already a Defendant.
Apollo, Blackstone, Bridgewater, and Bain Capital are all in the crosshairs of the same vishing campaign. Bain is already a defendant in the first sponsor-liability ruling. Two-front war on PE.
Executive Risk & Board Advisory