

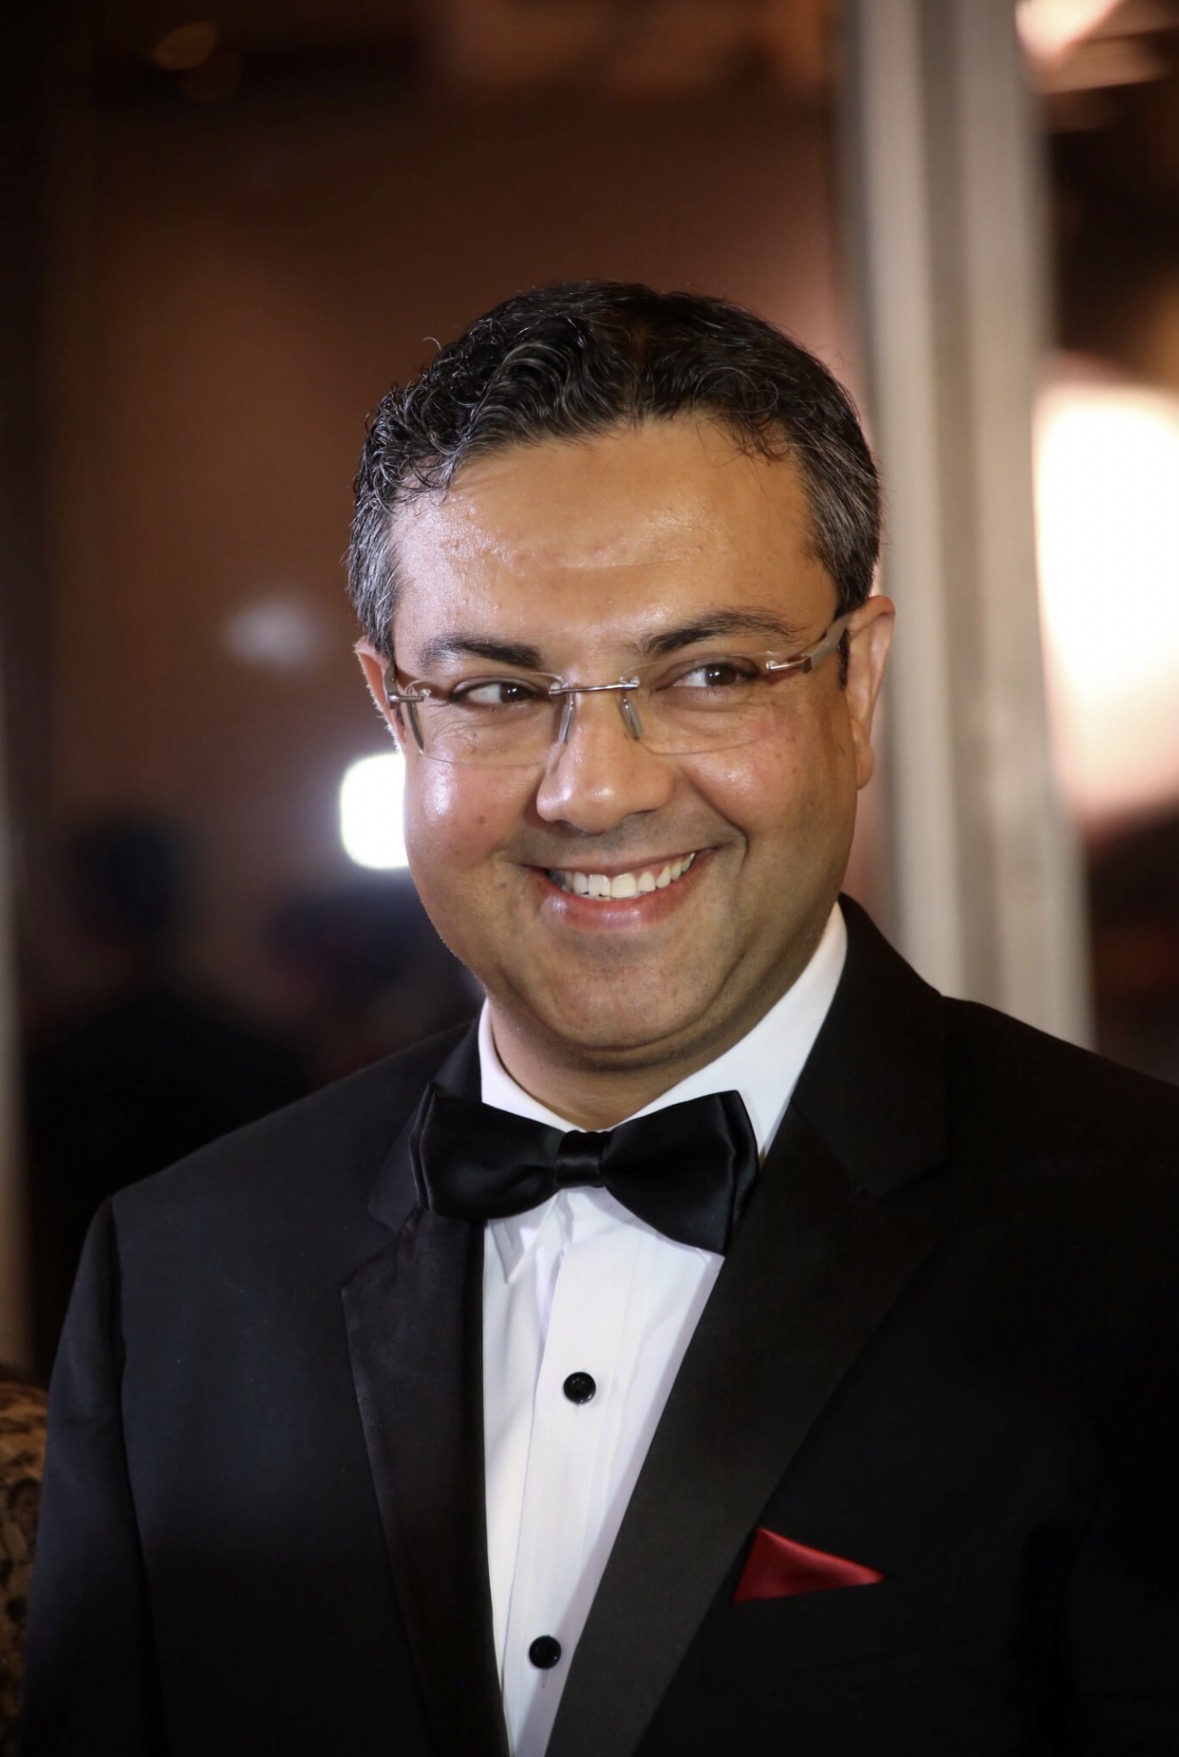
Dipan Mann
Founder, CEO & CTO
Dipan Mann is the founder and CEO of Cloudskope, an elite cybersecurity consulting firm that works with private equity sponsors, portfolio companies, boards, CFOs, and general counsel.
He began his career in the public sector. Before founding Cloudskope he held senior technology and customer experience leadership roles at LogicMonitor and LiveVox. He serves on the board of The Channel Company.
He writes most of what appears on this site: breach analysis, M&A cyber due diligence, and the questions boards should be asking before a deal closes rather than after. The recurring subject is the distance between assumed security and actual security, and who is holding the liability when the two turn out to be different.
Cloudskope is headquartered in Dallas and works with clients nationally. Connect on LinkedIn.


Take-Two Lost $2.8 Billion. The Hacker Cashed Out $250,000. Nobody Ever Sent a Ransom Note.
CyberLeek leaked GTA VI, pumped a memecoin, and cashed out $250K without ever demanding a ransom. What the first market-monetized extortion means for boards and deal teams.
Executive Risk & Board Advisory

Three Breaches, Three Years. Client Tax Records in a Hacker's Hands. EY Still Won't Name the Platform That Failed.
EY was breached a third time in three years, and this time the stolen files are client tax records. What boards and PE deal teams should be asking now.
Executive Risk & Board Advisory
Amazon's One Medical Confirms a "Limited" Breach. ShinyHunters Claims 8.8 Terabytes and a Deadline. Only One of Those Is Verified.
On June 13, One Medical disclosed unauthorized access to a third-party file storage system holding archived records from its legacy Iora Health and One Medical Seniors patients, describing the scope as a limited subset of files at nine named clinics. Days earlier, on June 18, ShinyHunters posted One Medical to its dark-web leak site, claimed 8.8 terabytes of stolen data, and gave the company until June 22 to begin negotiating before publication. ShinyHunters has released no sample data, so the claim is unverified. This is the same actor, the same playbook, and the same trust gap Cloudskope documented in the Canvas/Instructure breach: a company describing the smallest defensible version of events while a threat actor describes the largest. For boards in healthcare and any regulated-data business, the lesson is not which number to believe. It is to treat both as unproven until the evidence settles it, and to plan for the larger one.
Executive Risk & Board Advisory
Drift. Gainsight. Now Klue. And This Time, It Wasn't ShinyHunters.
For the third time in ten months, attackers drained Salesforce data through a trusted app. The first two were ShinyHunters. This one wasn’t — and that is why it matters.
Executive Risk & Board Advisory
Operation Epic Fury. Volt Typhoon. BRICS Settlement Rails. Your Portfolio's Cyber Risk Just Became a Geopolitical Position.
The convergence of Operation Epic Fury, Volt Typhoon's pre-positioned access inside US infrastructure, and BRICS de-dollarization is not a geopolitics story. It is a portfolio risk story. Ray Dalio calls this Stage 6 of the Big Cycle — the restructuring phase, where debt-laden empires compete through proxies and economic warfare rather than direct confrontation. Paul Kennedy called the underlying dynamic "imperial overstretch." Jared Diamond would note the resource pressure and institutional fragility. Thomas Friedman would observe that the world is no longer flat. For PE deal teams and portfolio operators, the relevant question is not who wins the geopolitical contest. It is which of your portcos are inside the blast radius of a conflict none of them signed up for.
Executive Risk & Board Advisory
Five Cyber Questions That Change What a Deal Is Worth.
Cyber due diligence is usually a checkbox near the end of the process. Five specific questions turn it into a deal-pricing input, surfacing the risks that actually move valuation and post-close cost.
Executive Risk & Board Advisory