

Dipan Mann
Founder, CEO & CTO
Dipan Mann is the founder and CEO of Cloudskope, an elite cybersecurity consulting firm that works with private equity sponsors, portfolio companies, boards, CFOs, and general counsel.
He began his career in the public sector. Before founding Cloudskope he held senior technology and customer experience leadership roles at LogicMonitor and LiveVox. He serves on the board of The Channel Company.
He writes most of what appears on this site: breach analysis, M&A cyber due diligence, and the questions boards should be asking before a deal closes rather than after. The recurring subject is the distance between assumed security and actual security, and who is holding the liability when the two turn out to be different.
Cloudskope is headquartered in Dallas and works with clients nationally. Connect on LinkedIn.


Acquisition Agreements Get Signed on Cyber Reps Nobody Verified. That Becomes the GC's Problem.
Acquisition agreements get signed on cyber reps no one independently verified. When the deal closes, the gap between what was repped and what's true becomes the buyer's liability and the GC's problem. What deal counsel should require first.
Executive Risk & Board Advisory
The First 100 Days After Close Decide Your Cyber Risk for the Whole Hold.
Cyber due diligence is a screen, not a clean bill of health. The day a deal closes, every undetected weakness becomes the sponsor's problem, and the first 100 days are the only window with the leverage to fix it.
Executive Risk & Board Advisory
Your Cyber Budget Is a Number. Your Cyber Risk Is a Distribution. CFOs Keep Confusing the Two.
Global cyber spending hit a record $219 billion in 2025, the same year breaches set their own record. The disconnect exposes the core CFO error: treating cybersecurity as a budget number instead of a loss distribution to reshape.
Executive Risk & Board Advisory
Four Breaches in Six Weeks. One Extortion Group. Your Portfolio Is the Target List.
ShinyHunters spent early 2026 running one pay-or-leak campaign through Instructure, Adobe, Match Group, and DentaQuest. The target profile is a near-perfect description of the average PE portfolio company.
Executive Risk & Board Advisory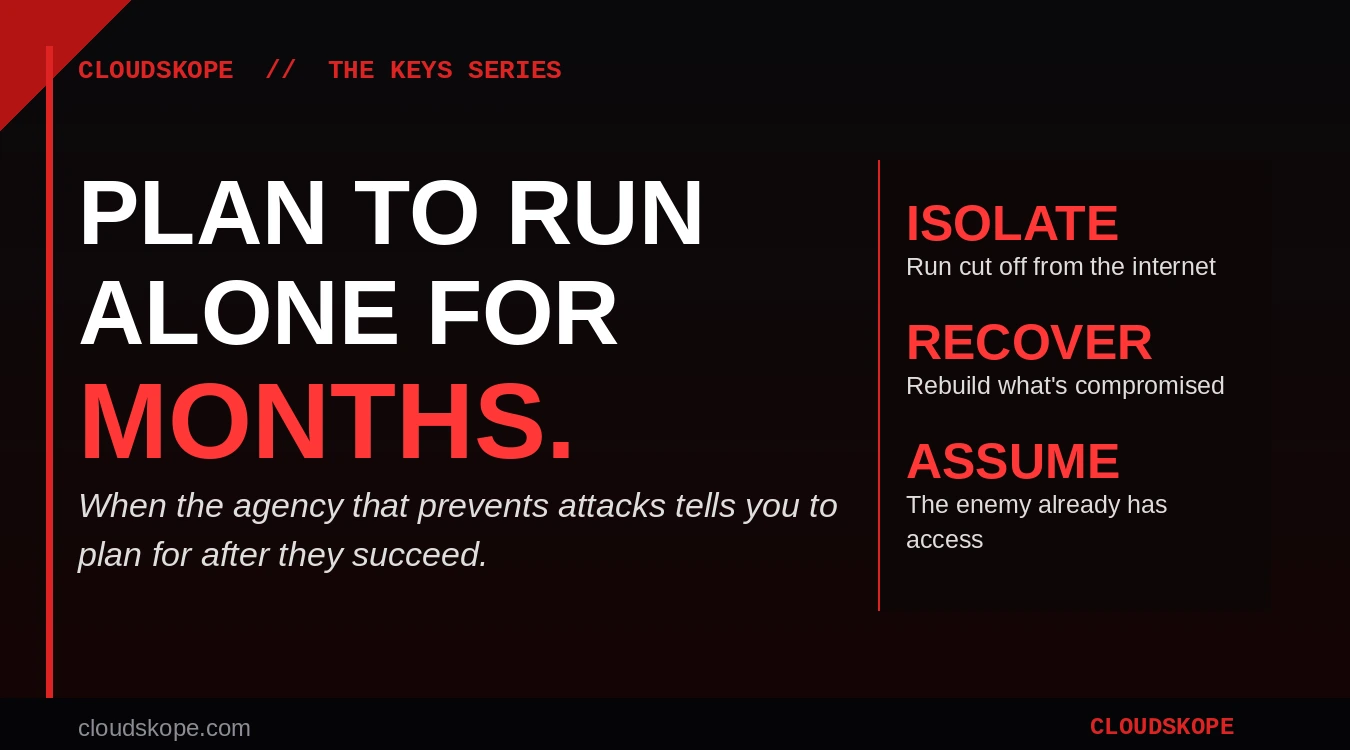
What CISA's CI Fortify Guidance Actually Means, and Why It Reads Like a Confession
CISA's CI Fortify guidance tells critical infrastructure to plan for months running cut off from its own networks, on the assumption the adversary is already inside. Why that reads like a confession.
Executive Risk & Board Advisory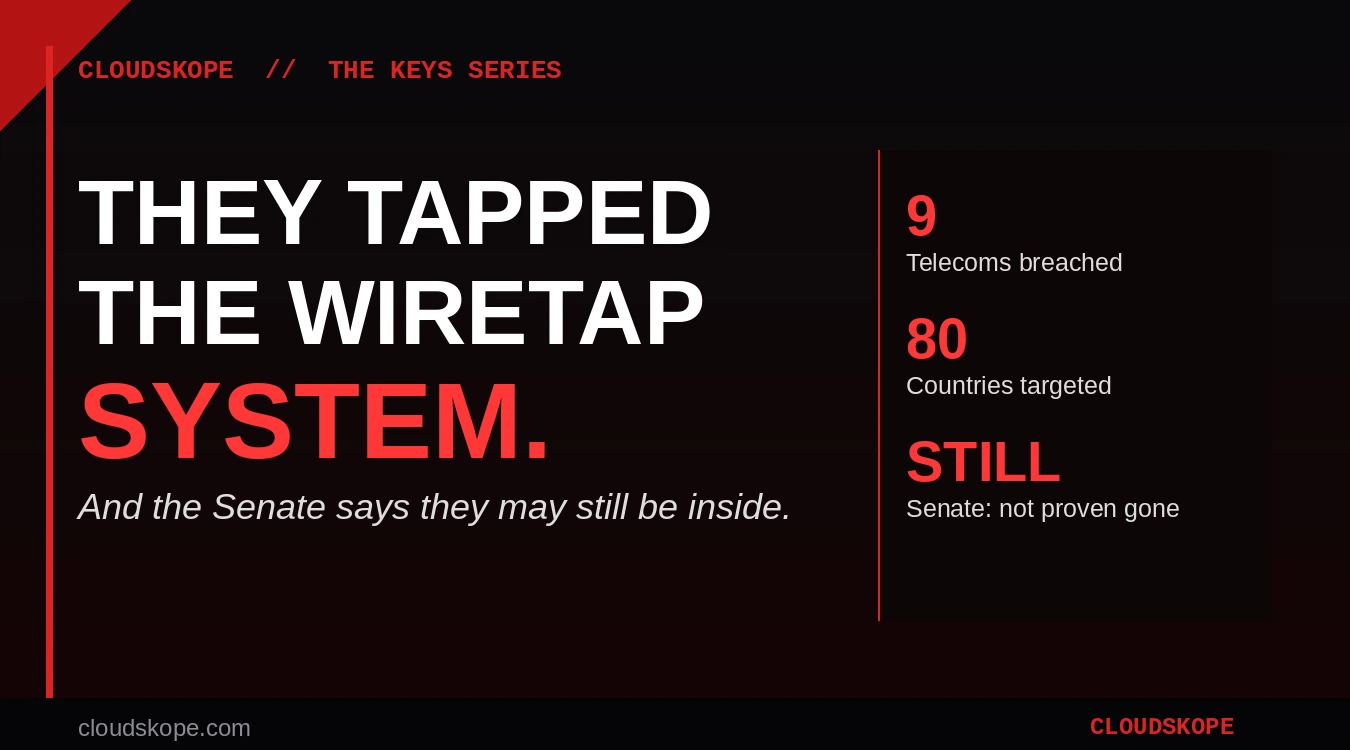
Still Inside: Why the Senate Says Salt Typhoon Was Never Fully Evicted
Salt Typhoon breached at least nine US carriers and the wiretap systems built for law enforcement. The Senate now says China's hackers were never fully evicted.
Executive Risk & Board Advisory