

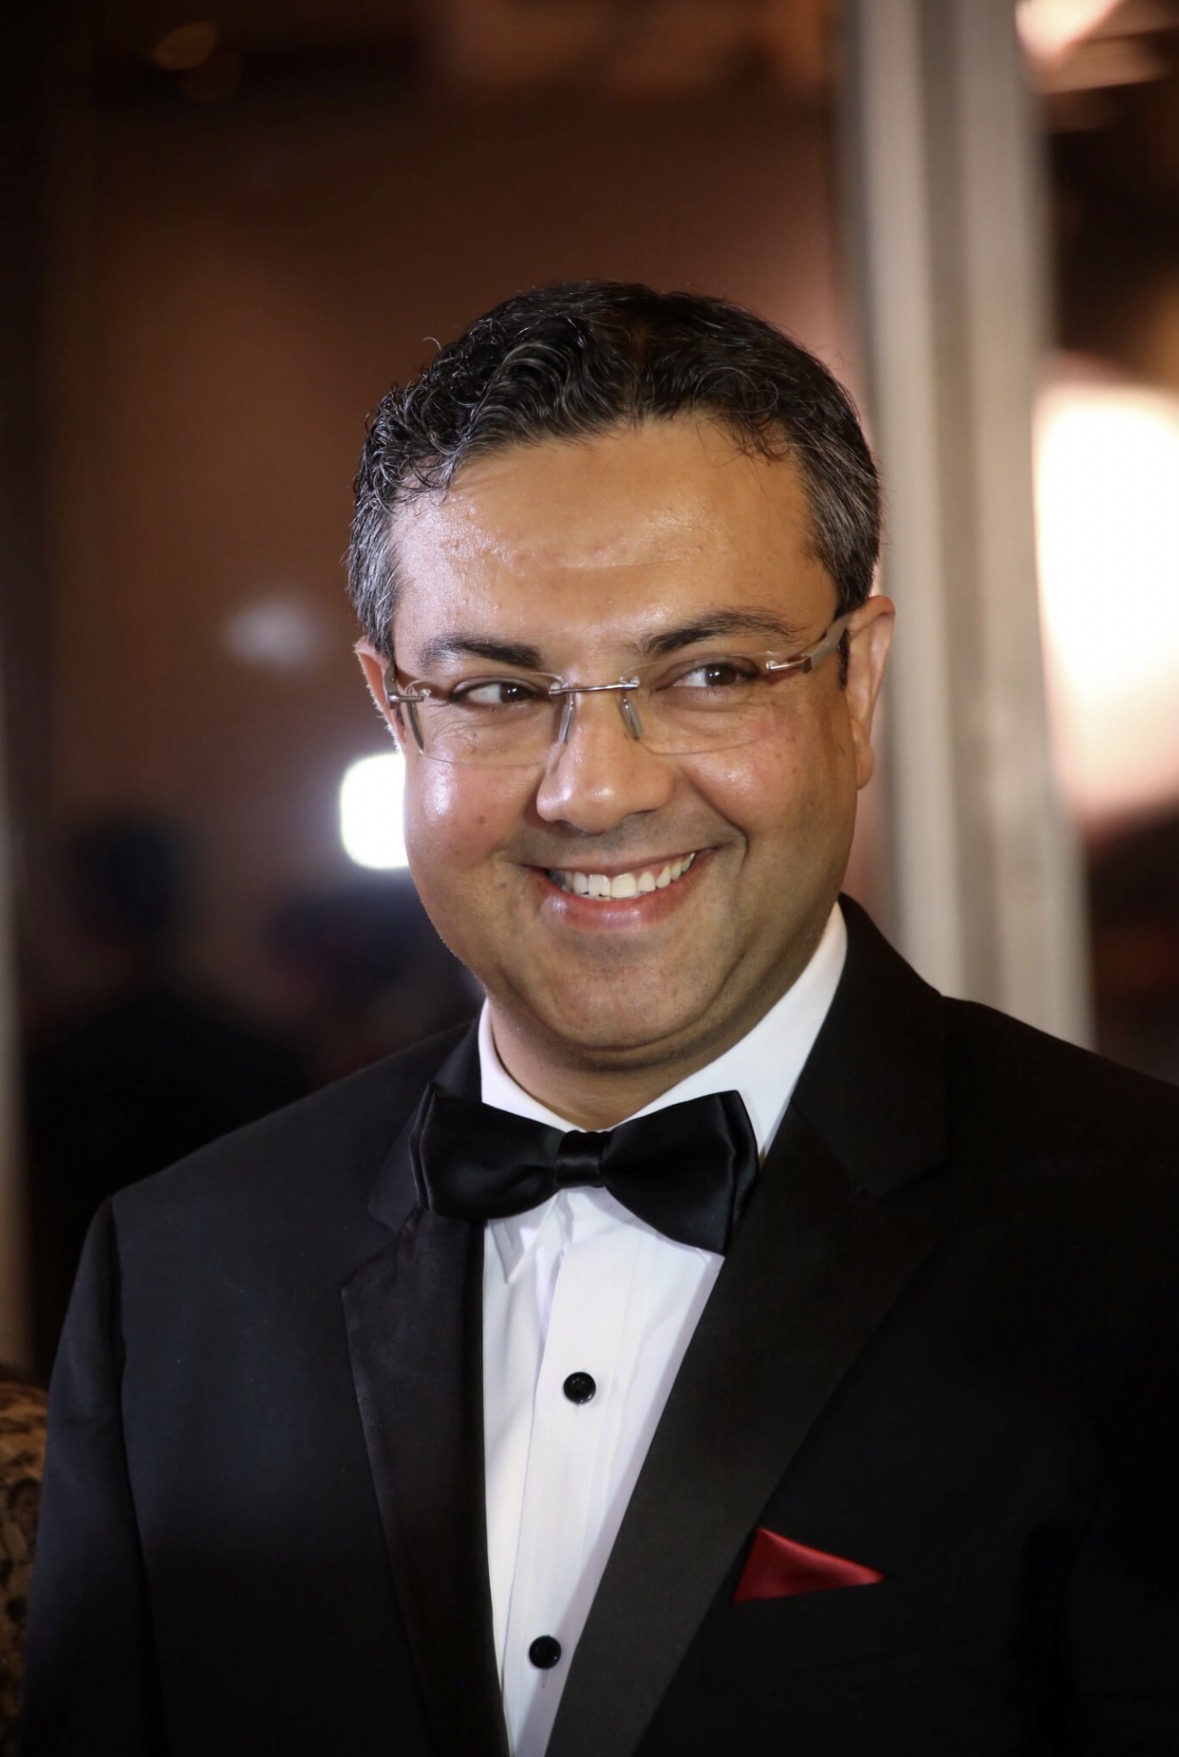
Dipan Mann
Founder, CEO & CTO
Dipan Mann is the founder and CEO of Cloudskope, an elite cybersecurity consulting firm that works with private equity sponsors, portfolio companies, boards, CFOs, and general counsel.
He began his career in the public sector. Before founding Cloudskope he held senior technology and customer experience leadership roles at LogicMonitor and LiveVox. He serves on the board of The Channel Company.
He writes most of what appears on this site: breach analysis, M&A cyber due diligence, and the questions boards should be asking before a deal closes rather than after. The recurring subject is the distance between assumed security and actual security, and who is holding the liability when the two turn out to be different.
Cloudskope is headquartered in Dallas and works with clients nationally. Connect on LinkedIn.


Instructure Paid Off Its Hackers. The House Homeland Security Committee Wants to Know Why.
On May 12, 2026, Instructure announced a settlement with the ShinyHunters criminal organization that breached its Canvas platform, claiming that all stolen data has been "returned" and that the threat actor has provided "digital confirmation of data destruction." The same day, the House Homeland Security Committee sent a letter to Instructure CEO Steve Daly requesting a briefing on the breach response and on the adequacy of coordination with federal law enforcement and CISA. A settlement is not a resolution. A promise from criminals is not a defensive posture. The pattern of conduct that produced three breaches in eight months has not been addressed. The students at 8,809 schools whose data was taken were not parties to the agreement that supposedly now protects them.
Executive Risk & Board Advisory
Phishing Statistics 2026: 20 Numbers Every Executive Should Know
20 phishing statistics from Verizon DBIR, IBM, FBI IC3, APWG, Microsoft, and Proofpoint that should change how every executive thinks about email security investment in 2026.
Executive Risk & Board Advisory
Audited. Compliant. Hacked Anyway.
$219 billion spent on cybersecurity in 2025. More major breaches than any year on record. Why every cybersecurity plan failed in 2026.
Executive Risk & Board Advisory
Most Common Passwords in 2026: What the Data Shows
The 2026 password data: 123456 is still #1, 65% of users reuse passwords across breaches. What boards and CISOs should be doing about it.
Executive Risk & Board Advisory
Cybersecurity Acronyms Glossary 2026
70+ cybersecurity acronyms decoded for executives, boards, and PE sponsors. MFA, EDR, MDR, ZTNA, NIST CSF, SOC 2, and the rest — organized across 11 categories.
Executive Risk & Board Advisory
30 Biggest Data Breaches of All Time
Ranked by records: Yahoo, NPD, LinkedIn, Marriott, Canvas, T-Mobile, Equifax, Target, Capital One, Change Healthcare — and the regulatory fallout each produced.
Threat Intelligence